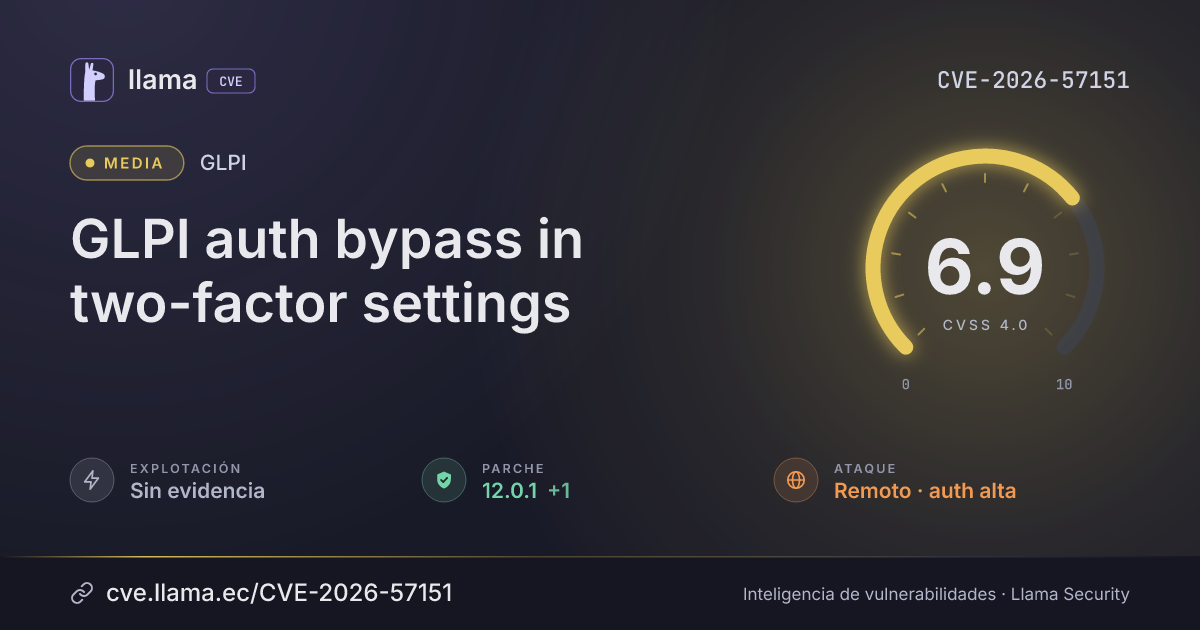
CVE-2026-57151
GLPI auth bypass in two-factor settings
A logged-in technician can turn off two-factor authentication for higher-privilege users or take control of it.
CVSS:4.0/AV:N/AC:L/AT:N/PR:H/UI:N/VC:N/VI:H/VA:N/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-57151 divulgada · CVSS 6.9 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Fuente: ENISA EUVD | Registro visto por primera vez en ENISA EUVD | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
GLPI, an IT asset and management software package, has a flaw in versions from 11.0.0 up to 11.0.10 and 12.0.1 that lets an authenticated technician change the two-factor authentication settings of a user with higher privileges, disabling that protection or taking control of it. The attack can be launched remotely over the network, but the attacker must already be logged in with a technician account.
Descripción original del registro (GitHub_M)
GLPI is a free asset and IT management software package. From 11.0.0 until 11.0.10 and 12.0.1, an authenticated technician can modify the two-factor authentication security of a user with higher privileges because the affected operations do not enforce all required authorization checks for the target user. This allows the technician to disable or take control of the higher-privileged user's two-factor authentication protection. This issue is fixed in versions 11.0.10 and 12.0.1.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
glpi |
Corregida | 11.0.10, 12.0.1 | — | — |
11.0.1012.0.1Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/glpi-project/glpi/security/advisories/GHSA-mhhg-77qx-qf26https://github.com/glpi-project/glpi/commit/c31c053b31950335f4f574b4c85dd0a07623b780https://github.com/glpi-project/glpi/releases/tag/11.0.10https://github.com/glpi-project/glpi/releases/tag/12.0.1Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.