llamaCVEVulnerability Intelligence
/
Vibe-Trading

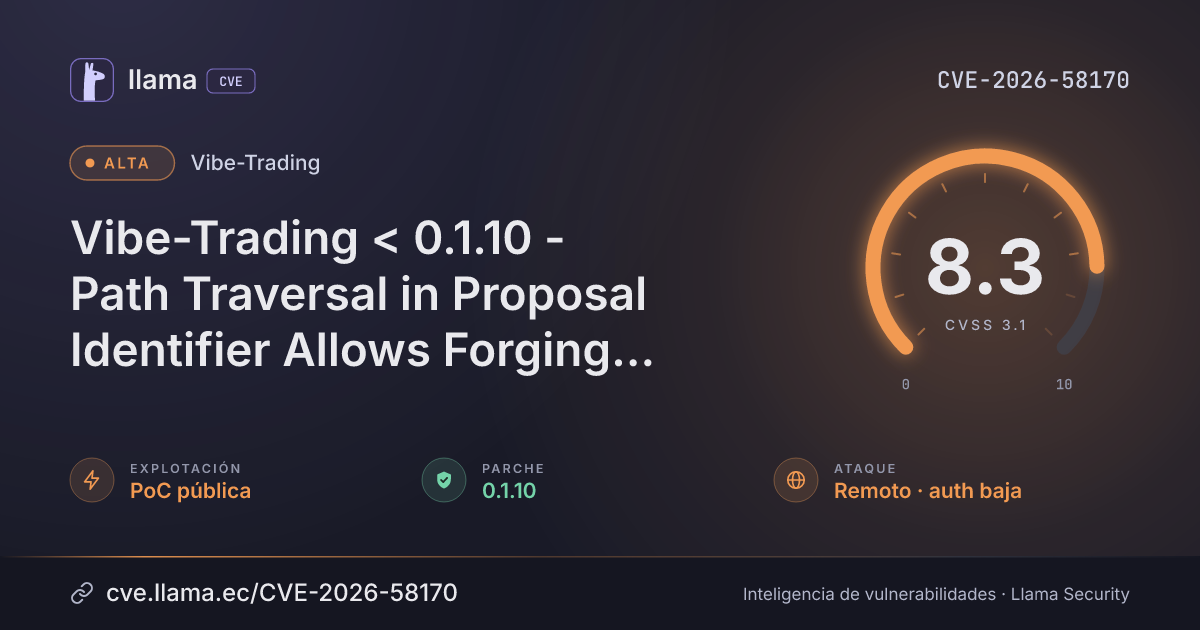
CVE-2026-58170

Vibe-Trading < 0.1.10 - Path Traversal in Proposal Identifier Allows Forging Live Trading Mandates

Specific setups onlyParche disponiblepath traversal
Descargar PNG JSON
CVSS 3.1
8.3
Alta
CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:H/A:H Fuente: CNA
ExplotaciónPoC públicaSSVC: poc · no figura en CISA KEV
Exploits públicos0Ninguno conocido
Parche1 versión0.1.10
Exposición141 dDesde la divulgación, 30 jun 2026, 10:53 a. m.
Detección125 dDesde la divulgación hasta su ingreso al índice
Decisión SSVCSeguir de cerca
Monitorear y programar la remediación
Existe PoC pública, no automatizable e impacto técnico parcial. Hay versiones corregidas disponibles.
Timeline

Ciclo de vida de la vulnerabilidad

Hoy
Divulgación
Publicada +1
Modificada
Explotación
Remediación
Monitoreo
Detectada
Fuente: OSV
Verificada
30 jun 26
3 nov 26
8 nov 26
16 nov 26
19 nov 26
30 jun 26
5 ago 26
9 sept 26
14 oct 26
19 nov 26
FechaFaseEventoDetalle
Divulgación Publicada CVE-2026-58170 divulgada · CVSS 8.3 (CNA)
Divulgación Evaluación SSVC CISA-ADP · explotación PoC pública
Monitoreo Detectada Ingresó al índice
Divulgación Modificada Última actualización del registro
Monitoreo Fuente: OSV Registro visto por primera vez en OSV
Monitoreo Verificada Última verificación contra las fuentes
Resumen

Vibe-Trading before 0.1.10 builds the proposal file path by joining a caller-supplied proposal identifier onto the broker proposals directory without sanitization (agent/src/live/mandate/commit.py). A proposal identifier containing path traversal sequences causes the application to load an attacker-controlled JSON file as an authoritative live trading mandate. Combined with the file upload endpoint, an admitted caller can write a JSON file to a known location and traverse to it, and because the ceilings validation is skipped when ceilings are absent, the attacker fully controls the committed mandate.

Affects Vibe-Trading versions before 0.1.10 when proposal JSON omits ceilings, which skips ceilings validation and lets a caller load attacker-controlled JSON as a live trading mandate. Fixed in 0.1.10.

¿Qué significa?Vibe-Trading builds the proposal file path by joining a caller-supplied proposal identifier without restricting it, which is a path traversal. Combined with the file upload endpoint, an admitted caller can write a JSON file to a known location and have it loaded as a live trading mandate, fully controlling the committed mandate.
¿Quién está afectado?Vibe-Trading versions before 0.1.10 are affected. The bug is reachable when the proposal JSON leaves out ceilings, because the ceilings validation is then skipped. To check a setup, compare the installed Vibe-Trading version with 0.1.10 and see whether proposal JSON is loaded without a ceilings field.
¿Qué hacer?Upgrade Vibe-Trading to 0.1.10 or later, which is the fixed version listed for this vulnerability.
Contexto

Condiciones y alcance

Condiciones necesarias para que el fallo sea explotable
01
Vibe-Trading versions before 0.1.10“Vibe-Trading before 0.1.10 builds the proposal file path by joining a caller-supplied proposal identifier”
02
Ceilings validation is skipped when ceilings are absent from the proposal JSON“because the ceilings validation is skipped when ceilings are absent”
03
Combined with the file upload endpoint, so the attacker can write the JSON file to a known location“Combined with the file upload endpoint, an admitted caller can write a JSON file to a known location”
Vector CVSS 3.1

Desglose de métricas

Opción resaltada = valor del vector · izquierda = peor caso · CNA
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:L
BajaAlta
PrivilegiosPR:L
NingunoBajosAltos
InteracciónUI:N
NingunaRequerida
AlcanceS:U
CambiadoSin cambio
ConfidencialidadC:L
AltoBajoNinguno
IntegridadI:H
AltoBajoNinguno
DisponibilidadA:H
AltoBajoNinguno
Versiones

Rangos afectados

Afectada Corregida
Vibe-Trading< 0.1.10
0.1.10
Remediación

Estado del parche por paquete

Paquete / productoEstadoCorregida enDesde divulgaciónÚltima versión
Vibe-Trading
Corregida 0.1.10 — —
Versiones corregidas0.1.10
Explotación

Arsenal público

Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.

Registro
EscenarioGENERALVulnCheck
Referencias
Parchehttps://github.com/HKUDS/Vibe-Trading/pull/256
Parchehttps://github.com/HKUDS/Vibe-Trading/commit/0ab701302f90e701c9dc558a898a217a376610c3
Otrahttps://github.com/HKUDS/Vibe-Trading/releases/tag/v0.1.10
Otrahttps://www.vulncheck.com/advisories/vibe-trading-path-traversal-in-proposal-identifier-allows-forging-live-trading-mandates

Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.