llamaCVEVulnerability Intelligence
/
WordPress

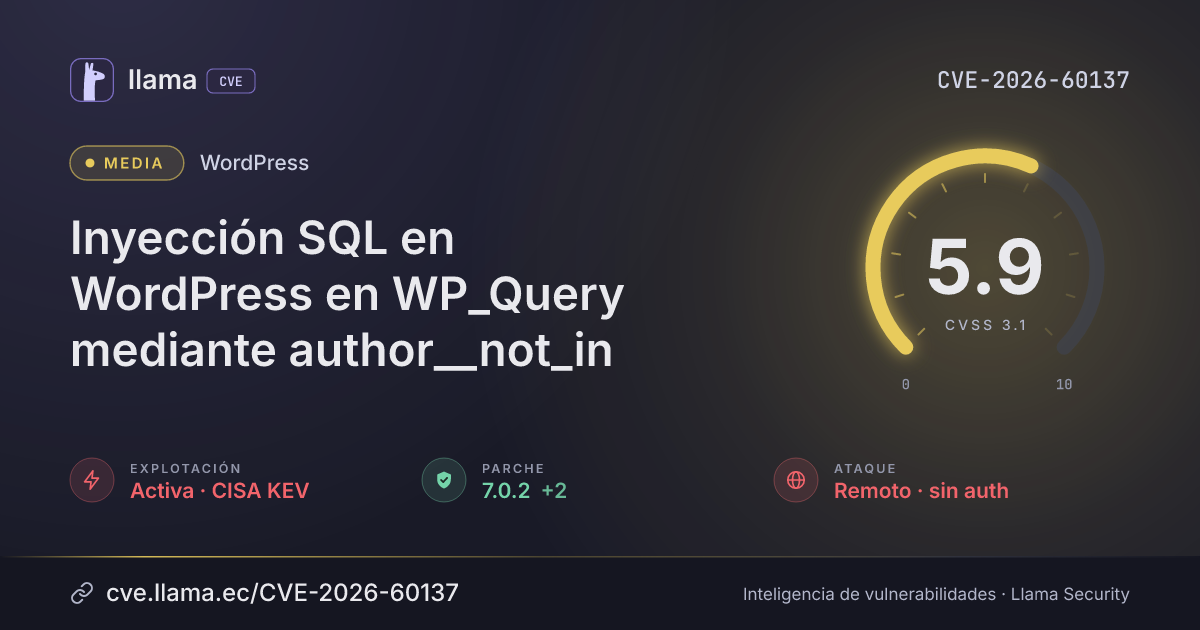
CVE-2026-60137

WordPress SQL injection in WP_Query via author__not_in

An attacker can inject SQL to read or modify the site's database through untrusted input in author__not_in.

CISA KEV · explotación activaCrítica · en CISA KEVParche disponible
Descargar PNG JSON
CVSS 3.1
5.9
Media
CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:U/C:H/I:N/A:N Fuente: CNA
ExplotaciónActivaEn CISA KEV desde 21 jul 2026
Exploits públicos0Explotada, pero sin código público enlazado
Parche3 versiones6.8.6 · 6.9.5 · 7.0.2
Exposición126 dDesde la divulgación, 17 jul 2026, 2:14 p. m.
Detección97 dDesde la divulgación hasta su ingreso al índice
Decisión SSVCAtender
Priorizar en el próximo ciclo de cambios
Explotación activa (CISA KEV), no automatizable e impacto técnico total. Plazo KEV: 4 ago 2026.
Timeline

Ciclo de vida de la vulnerabilidad

Hoy
Divulgación
Publicada
Evaluación SSVC
Modificada
Explotación
CISA KEV
Remediación
Plazo KEV
Monitoreo
Detectada
Verificada
17 jul 26
21 jul 26
22 jul 26
4 ago 26
7 oct 26
22 oct 26
19 nov 26
21 nov 26
17 jul 26
18 ago 26
19 sept 26
20 oct 26
21 nov 26
FechaFaseEventoDetalle
Divulgación Publicada CVE-2026-60137 divulgada · CVSS 5.9 (CNA)
Explotación CISA KEV Agregada al catálogo de vulnerabilidades explotadas
Divulgación Evaluación SSVC CISA-ADP · explotación activa
Remediación Plazo KEV Fecha límite de remediación para agencias federales (EE. UU.)
Divulgación Modificada Última actualización del registro
Monitoreo Detectada Ingresó al índice
Monitoreo Verificada Última verificación contra las fuentes
Resumen
Resumen generado por IA · CC-BY 4.0 · 18 nov 2026

WordPress has a SQL injection flaw in how it handles the author__not_in parameter of WP_Query, which an attacker can reach remotely without logging in when a plugin or theme passes untrusted input to that parameter. On newer releases, it can be combined with a REST API batch-route confusion issue to achieve remote code execution, and attacks using it are happening.

Affects WordPress 6.8.0–6.8.5, 6.9.0–6.9.4 and 7.0.0–7.0.1 (and 7.1 beta before beta2). Fixed in 6.8.6, 6.9.5 and 7.0.2.

¿Qué significa?A flaw in how WP_Query handles the author__not_in parameter allows SQL injection. On WordPress 6.9 and higher, combined with a REST API batch-route confusion issue, it leads to remote code execution.
¿Quién está afectado?Affected ranges are WordPress 6.8.0–6.8.5, 6.9.0–6.9.4 and 7.0.0–7.0.1, plus 7.1 beta before beta2. The installed version appears in the WordPress dashboard (Updates screen) or in the admin footer, and can be compared against these ranges.
¿Qué hacer?Update to a fixed release for the installed branch: 6.8.6, 6.9.5 or 7.0.2. The facts give no workaround.
Descripción original del registro

WordPress 6.8.x before 6.8.6, 6.9.x before 6.9.5, and 7.0.x before 7.0.2 does not properly sanitise the author__not_in parameter of WP_Query, which could allow SQL Injection when a plugin or theme passes untrusted input to the parameter.

Contexto

Condiciones y alcance

Condiciones necesarias para que el fallo sea explotable
01
WordPress 6.8.0–6.8.5, 6.9.0–6.9.4, or 7.0.0–7.0.1 (and 7.1 beta before beta2)“6.8.0 - 6.8.5”
02
On 6.9 and higher, combined with a REST API batch-route confusion issue, this leads to remote code execution“In WordPress versions 6.9 and higher, this combined with a REST API batch-route confusion issue”
¿Quién debe revisar?Teams running WordPress 6.8, 6.9 or 7.0 sites, especially those with plugins or themes passing untrusted input to WP_Query author__not_in.
Vector CVSS 3.1

Desglose de métricas

Opción resaltada = valor del vector · izquierda = peor caso · CNA
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:H
BajaAlta
PrivilegiosPR:N
NingunoBajosAltos
InteracciónUI:N
NingunaRequerida
AlcanceS:U
CambiadoSin cambio
ConfidencialidadC:H
AltoBajoNinguno
IntegridadI:N
AltoBajoNinguno
DisponibilidadA:N
AltoBajoNinguno
Score de explotaciónQué tan fácil y probable es que la exploten
10.0/ 10Muy alto
Vector 7.1 (fácil) · +2.9 por explotación activa.
Versiones

Rangos afectados

Afectada Corregida
WordPress≥ 6.8.0 < 6.8.6
WordPress≥ 6.9.0 < 6.9.5
WordPress≥ 7.0.0 < 7.0.2
6.8.0
6.8.6
6.9.0
6.9.5
7.0.0
7.0.2
Remediación

Estado del parche por paquete

Paquete / productoEstadoCorregida enDesde divulgaciónÚltima versión
WordPress
Corregida 6.8.6, 6.9.5, 7.0.2 — —
Versiones corregidas6.8.66.9.57.0.2
Explotación

Arsenal público

Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.

Referencias
Fabricantehttps://github.com/WordPress/wordpress-develop/security/advisories/GHSA-fpp7-x2x2-2mjf
Fabricantehttps://wordpress.org/news/2026/07/wordpress-7-0-2-release/

Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.