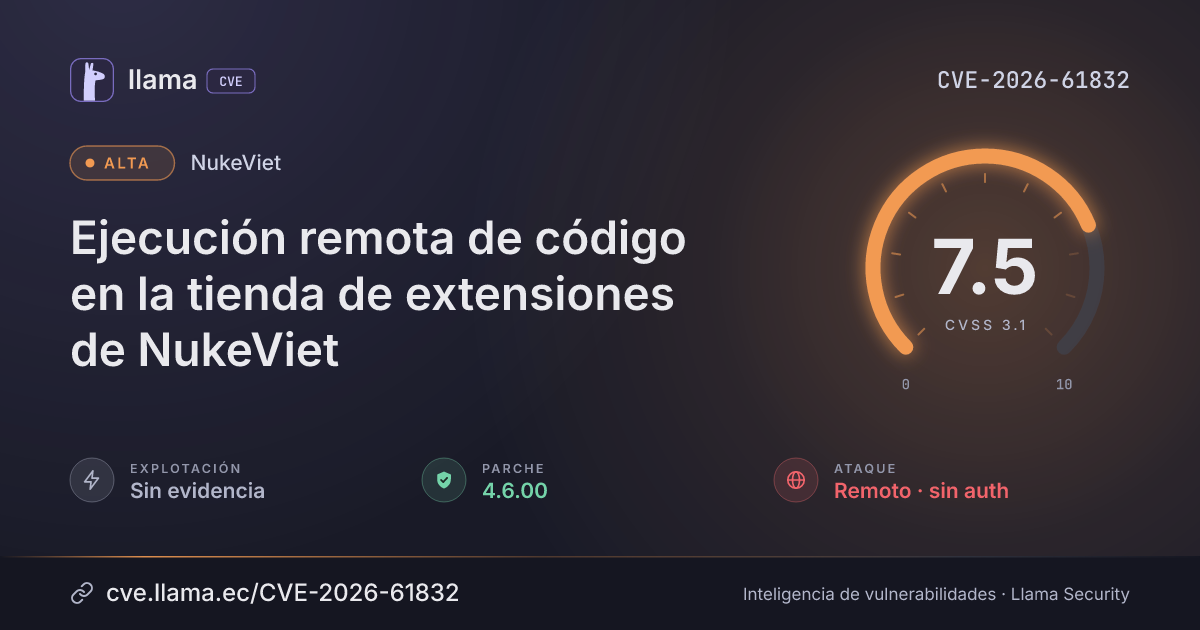
CVE-2026-61832
NukeViet remote code execution in extension store
An attacker who can alter traffic to the extension store can run code on the server as the web server user.
Texto original en inglés · Ver en español
CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:U/C:H/I:H/A:H
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-61832 divulgada · CVSS 7.5 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
A remote attacker who can alter traffic to the NukeViet CMS extension store, without logging in, can run code on the server as the web-server user. The attack works when a GODADMIN opens or uses the store's list, detail, install, or update functions, which causes the server to process a substituted response that writes a PHP file under the web root.
Affects NukeViet 4.x installations before 4.6.00 when a GODADMIN administrator uses the extension store. Fixed in 4.6.00.
Descripción original del registro (GitHub_M)
NukeViet CMS is a multi Content Management System. Prior to 4.6.00, a network attacker who can alter outbound traffic to the extension store can exploit the HTTP client's disabled sslverify setting to substitute a serialized response. Extension-store handlers pass the response to unserialize() without an allowed_classes restriction, allowing an in-tree GuzzleHttp\Cookie\FileCookieJar gadget to write attacker-controlled content to a chosen path. When a GODADMIN opens or uses the store list, detail, install, or update functions, the substituted response can write a PHP file under the web root and execute code as the web-server user. This issue is fixed in version 4.6.00.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
nukeviet |
Corregida | 4.6.00 | — | — |
4.6.00Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/nukeviet/nukeviet/security/advisories/GHSA-9xfw-vx6g-wpmmhttps://nukeviet.vn/vi/news/Tin-tuc/thong-bao-phat-hanh-nukeviet-4-6-00-855.htmlhttps://github.com/nukeviet/nukeviet/commit/099ec8cc4734ba8c1b871653ee454367a07446cchttps://github.com/nukeviet/nukeviet/releases/tag/4.6.00Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.