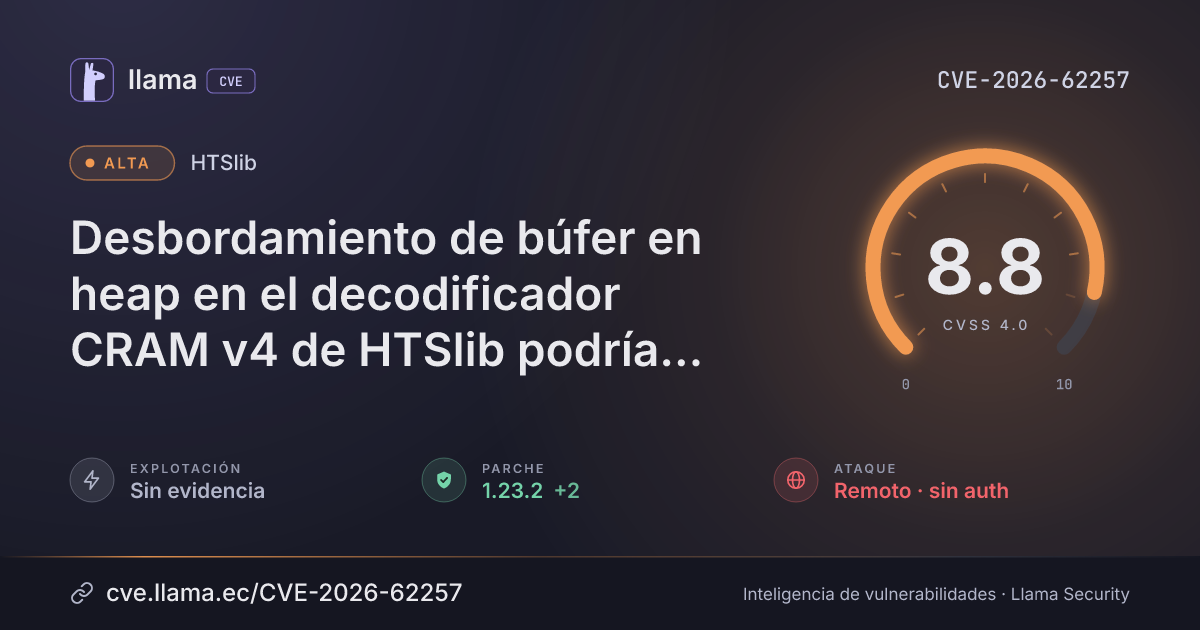
CVE-2026-62257
HTSlib heap overflow in CRAM v4 decoder may allow code execution
An attacker can send a crafted file to crash the program or corrupt memory, possibly running arbitrary code.
CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:N/VI:H/VA:L/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-62257 divulgada · CVSS 8.8 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
HTSlib, a library for reading and writing bioinformatics file formats, has a heap memory overflow in its experimental CRAM v4 decoder. An attacker can trigger it remotely, without logging in or any user action, by supplying a crafted file, which may crash the program or corrupt heap memory in a way that could allow arbitrary code execution.
Affects HTSlib before 1.21.2, 1.22.0 to 1.22.2, and 1.23.0 to 1.23.1 when decoding CRAM v4 files with the experimental XPACK or XRLE decoders. Fixed in 1.21.2, 1.22.3 and 1.23.2.
Descripción original del registro (GitHub_M)
HTSlib is a library for reading and writing bioinformatics file formats. Prior to 1.21.2, 1.22.3, 1.23.2, and 1.24, the experimental CRAM v4 XPACK and XRLE decoders cache expanded block pointers at indexes beyond the 512-element slice->block_by_id array. An array index partially controlled by data in the input file first causes an out-of-bounds read to determine whether a block is cached; a null value then causes allocation of a block and an out-of-bounds pointer write to the same element. The invalid read may crash the process, while the write may corrupt heap state and could permit arbitrary code execution. This issue is fixed in versions 1.21.2, 1.22.3, 1.23.2, and 1.24.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
htslib |
Corregida | 1.21.2, 1.22.3, 1.23.2 | — | — |
1.21.21.22.31.23.2Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/samtools/htslib/security/advisories/GHSA-6q7c-m967-9v37https://github.com/samtools/htslib/pull/2020https://github.com/samtools/htslib/pull/2046https://github.com/samtools/htslib/commit/a3e8dca14dcfdc6167281721ede6d6ecd3395badhttps://github.com/samtools/htslib/commit/c0b50372ed133c650fa0a641607da5cde46bcd8chttps://github.com/samtools/htslib/commit/d66a77dbf8f52f7f44efd7929a28b94bbfc17f2fhttps://github.com/samtools/htslib/releases/tag/1.21.2https://github.com/samtools/htslib/releases/tag/1.22.3https://github.com/samtools/htslib/releases/tag/1.23.2https://github.com/samtools/htslib/releases/tag/1.24Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.