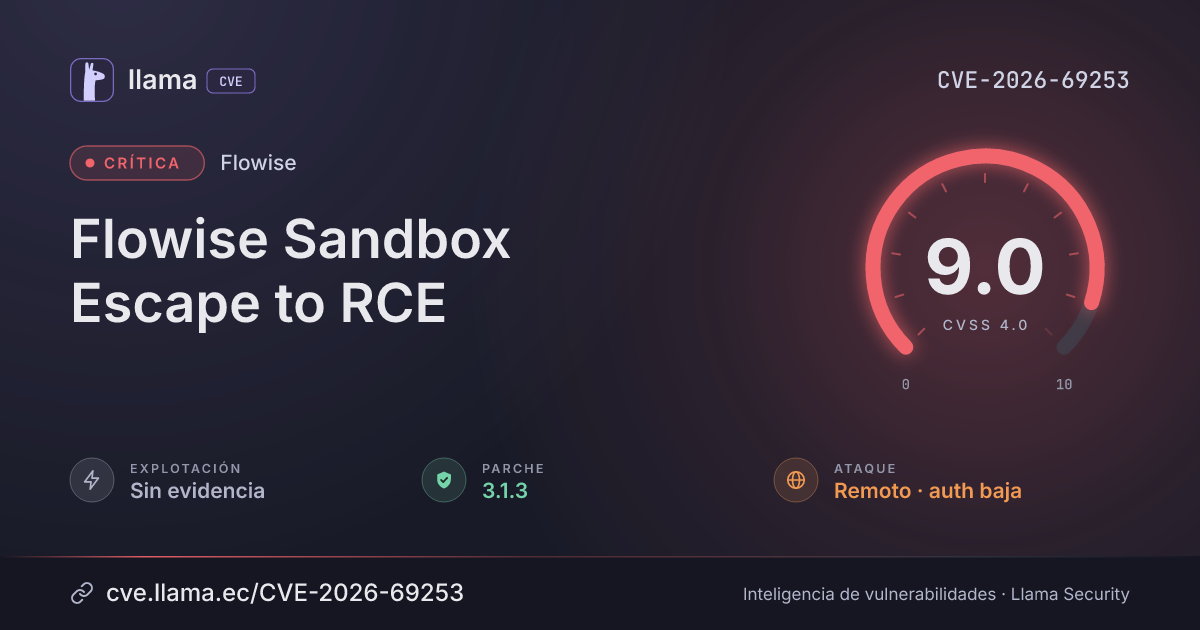
CVSS:4.0/AV:N/AC:H/AT:N/PR:L/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H
Fuente: CNA
CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:HCiclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 3.1.3 | flowise · -40 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-69253 divulgada · CVSS 9 (CNA) | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Flowise is a drag-and-drop user interface for building customized large language model (LLM) flows. Prior to version 3.1.3, several custom-tool components — AgentAsTool, ChatflowTool, and ExecuteFlow — ran code in the in-process vm2 sandbox. To build that code, they inserted a user-controlled baseURL value straight into the JavaScript source, for example const url = "${baseURL}/..."; . The only check on baseURL was isValidURL , but a valid-looking URL can still contain characters that break out of a code string. An authenticated user could craft a baseURL that passed this check, closed the surrounding string, and injected their own JavaScript into the sandboxed script (code injection, CWE-94). The vm2 sandbox runs in the same Node.js process as Flowise and exposes risky dependencies. As a result, the injected code could escape the sandbox and run arbitrary code on the Flowise server as the Flowise process user. Exploitation only requires an authenticated session. The issue is fixed in version 3.1.3, which passes the URL to the sandbox as data instead of inserting it into code and adds stricter URL validation.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
npmflowise |
Corregida | 3.1.3 | -40 d | 3.1.4 no afectada |
npmflowise-components |
Corregida | 3.1.3 | -40 d | 3.1.4 no afectada |
3.1.3Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/FlowiseAI/Flowise/security/advisories/GHSA-wg86-r78f-74mphttps://github.com/FlowiseAI/Flowise/pull/6417https://github.com/FlowiseAI/Flowise/commit/3f257bdc8196082a178da7134a075824401b13b9https://github.com/FlowiseAI/Flowise/releases/tag/flowise@3.1.3Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.