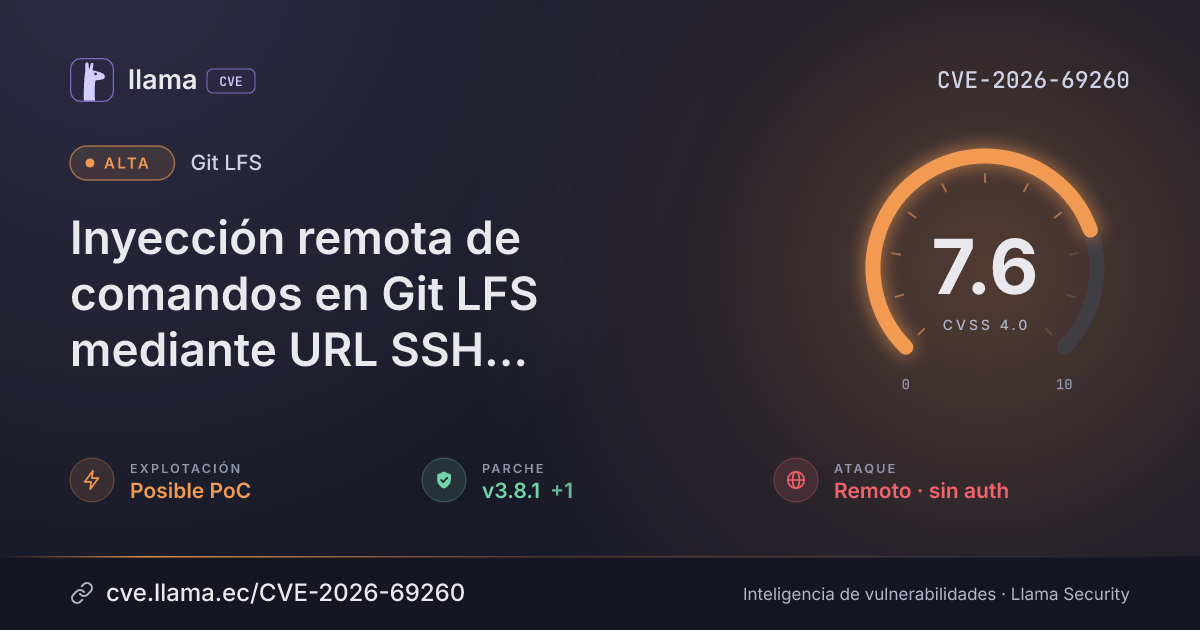
CVE-2026-69260
Git LFS remote command injection via crafted SSH URLs
A remote attacker can run arbitrary commands on a user's computer if they clone from a crafted SSH URL.
CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:P/VC:H/VI:H/VA:N/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche v3.8.1 | github.com/git-lfs/git-lfs/v3 · -29 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-69260 divulgada · CVSS 7.6 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Fuente: ENISA EUVD | Registro visto por primera vez en ENISA EUVD | |
| Monitoreo | Fuente: PoC-in-GitHub | Registro visto por primera vez en PoC-in-GitHub | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Git LFS, a Git extension for versioning large files, can be made to run arbitrary commands through crafted SSH URLs. An attacker on the network can trigger this remotely without logging in, but it requires a user to take an action and depends on the remote Git LFS service passing received commands to a shell without adequate sanitization.
Affects Git LFS 0.5.0 through 2.13.3 and 3.0.0 through 3.8.0 when it uses SSH remotes and the remote host passes received commands to a shell without sanitizing them. Fixed in 3.8.1.
Descripción original del registro (GitHub_M)
Git LFS is a Git extension for versioning large files. From 0.5.0 until 3.8.1, Git LFS does not format the SSH URL path component as a single argument when constructing remote object-transfer or authentication commands. Shell metacharacters in the SSH URL can therefore escape the intended path argument and cause arbitrary command execution when the remote Git LFS service passes received commands to a shell without adequate sanitization. Git LFS also incorrectly encodes default HTTPS URLs when an SSH URL is configured and the remote host either does not support Git LFS remote commands over SSH or supports HTTP authentication over SSH but git-lfs-authenticate does not return an explicit HTTP URL. This issue is fixed in version 3.8.1.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
gogithub.com/git-lfs/git-lfs |
Sin parche | — | — | v2.5.2+incompatible afectada |
gogithub.com/git-lfs/git-lfs/v3 |
Corregida | v3.8.1 | -29 d | v3.8.1 no afectada |
3.8.1v3.8.1Arsenal público
Ver los 1 repositorios de GitHub
Los repositorios públicos incluyen exploits, escáneres, laboratorios y reglas de detección. No ejecute código de terceros sin revisarlo en un entorno aislado.
https://github.com/git-lfs/git-lfs/security/advisories/GHSA-w3f2-pr6x-wwjchttps://github.com/googlesky/CVE-2026-69260https://github.com/git-lfs/git-lfs/commit/091a95a796739bd0b8f59d8deeea79a452959508https://github.com/git-lfs/git-lfs/commit/92d81117d465469a61dcb78546dd3d88806b25fdhttps://github.com/git-lfs/git-lfs/commit/af5f4579ac1155734bb08f00ca92b9e89f8b51dfhttps://github.com/git-lfs/git-lfs/commit/d90ed66f2d465f8b3ba5fd6e4ac3c711c9e0a2d6https://github.com/git-lfs/git-lfs/releases/tag/v3.8.1Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.