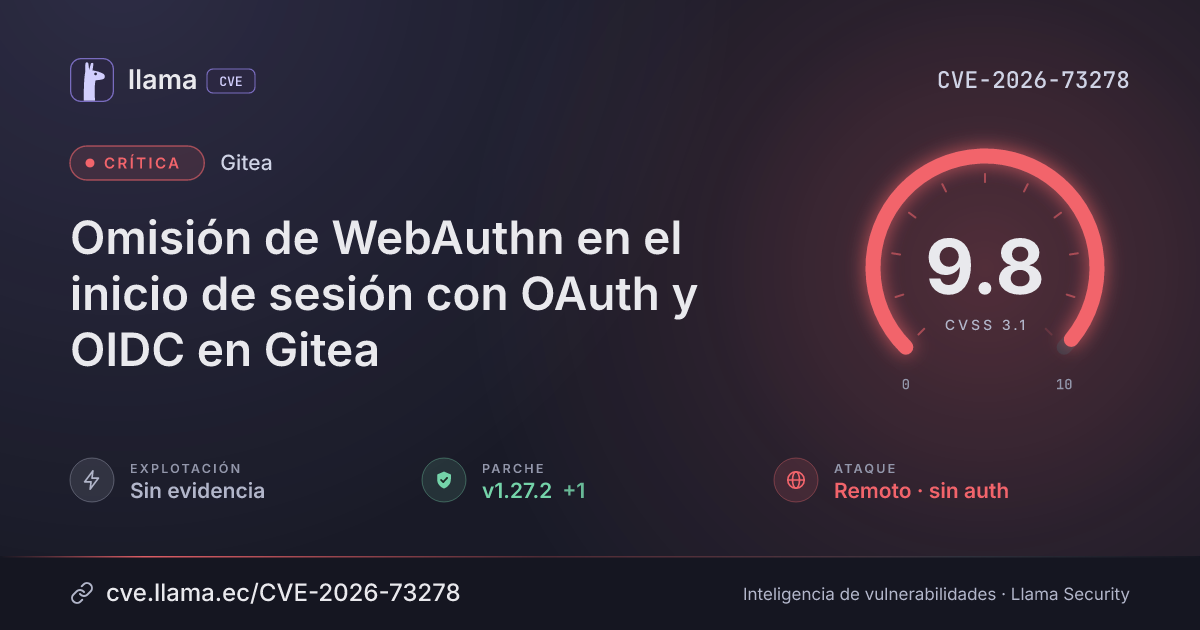
CVE-2026-73278
Gitea WebAuthn bypass during OAuth and OIDC sign-in
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H
Fuente: CISA-ADP
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche v1.27.2 | gitea.dev · -54 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-73278 divulgada · CVSS 9.8 (CISA-ADP) | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: OSV | Registro visto por primera vez en OSV | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Gitea's OAuth2 and OpenID Connect sign-in paths do not require a WebAuthn challenge when WebAuthn is the account's only configured second factor. A party able to authenticate through the affected external identity flow can obtain a full session without the passkey verification enforced during password login. One affected path can also persist an external identity link, extending the compromise beyond the initial session; accounts with TOTP configured are outside the reported WebAuthn-only scenario.
Affects Gitea 1.16.0 through 1.27.1 for accounts that use WebAuthn as the only second factor (no TOTP) and sign in through OAuth2 or OpenID Connect. Fixed in 1.27.2.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
gogitea.dev |
Corregida | v1.27.2 | -54 d | v1.27.3 no afectada |
1.27.2v1.27.2Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/go-gitea/gitea/security/advisories/GHSA-92j2-6qcg-c28chttps://blog.gitea.com/release-of-1.27.2/https://github.com/go-gitea/gitea/pull/38805https://github.com/go-gitea/gitea/pull/38810https://github.com/go-gitea/gitea/releases/tag/v1.27.2Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.