llamaCVEVulnerability Intelligence
/
Hitachi HiRDB Server

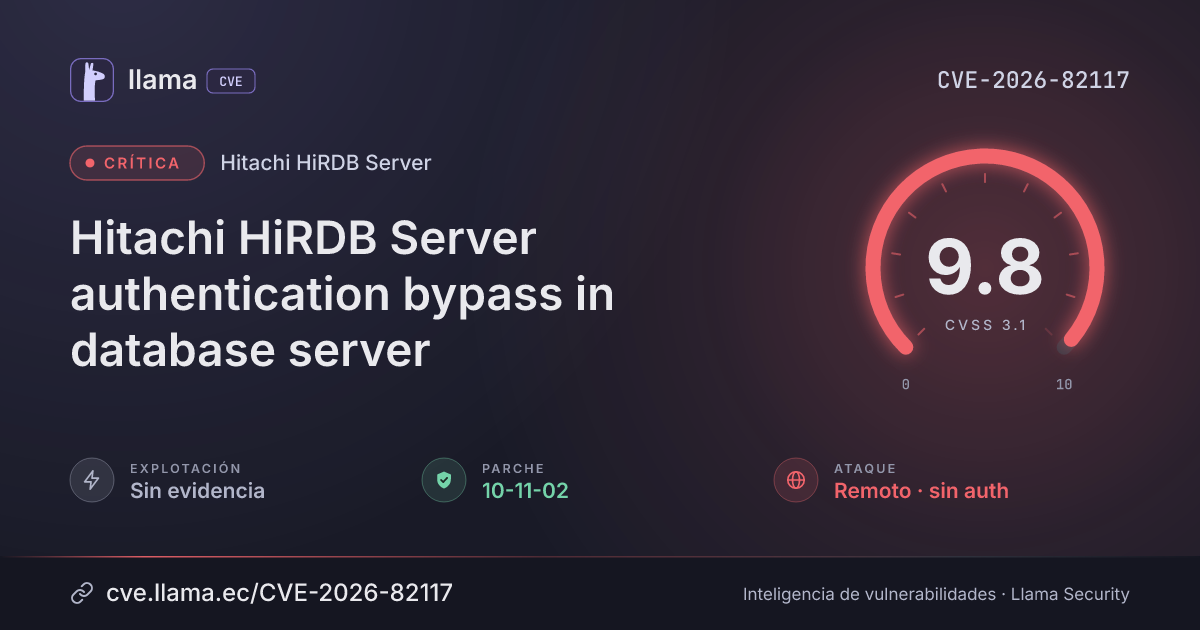
CVE-2026-82117

Hitachi HiRDB Server authentication bypass in database server

An attacker can spoof an identity to bypass login checks and gain unauthorized access to the database.

UnclearParche disponibleauthentication bypass
Descargar PNG JSON
CVSS 3.1
9.8
Crítica
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H Fuente: CNA
ExplotaciónSin evidenciaSSVC: none · no figura en CISA KEV
Exploits públicos0Ninguno conocido
Parche1 versión10-11-02
Exposición23 dDesde la divulgación, 27 oct 2026, 4:37 a. m.
Detección7 minDesde la divulgación hasta su ingreso al índice
Decisión SSVCAtender
Priorizar en el próximo ciclo de cambios
Sin explotación conocida, automatizable e impacto técnico total. Hay versiones corregidas disponibles.
Timeline

Ciclo de vida de la vulnerabilidad

Hoy
Divulgación
Publicada
Evaluación SSVC +1
Explotación
Remediación
Monitoreo
Detectada +2
Verificada
27 oct 26
4 nov 26
16 nov 26
19 nov 26
27 oct 26
2 nov 26
7 nov 26
13 nov 26
19 nov 26
FechaFaseEventoDetalle
Divulgación Publicada CVE-2026-82117 divulgada · CVSS 9.8 (CNA)
Monitoreo Detectada Ingresó al índice
Monitoreo Fuente: NIST NVD Registro visto por primera vez en NIST NVD
Monitoreo Fuente: ENISA EUVD Registro visto por primera vez en ENISA EUVD
Divulgación Evaluación SSVC CISA-ADP · explotación ninguna
Divulgación Modificada Última actualización del registro
Monitoreo Verificada Última verificación contra las fuentes
Resumen
Resumen generado por IA · CC-BY 4.0

The HiRDB database server software is affected, including its Version 9 and Version 10 editions and the related additional-function and 32-bit variants. An attacker could spoof an identity to bypass authentication, potentially gaining unauthorized access to the database.

HiRDB Server Versions 9 and 10 and their Additional Function builds, as listed by Hitachi, are affected. Version 10 is fixed in 10-11-02, and the facts give no vendor rating or fix for Version 9.

¿Qué significa?The vulnerability lets an attacker bypass authentication by spoofing. In plain terms, a request can get past the login check by pretending to be a legitimate user or source.
¿Quién está afectado?Hitachi lists HiRDB Server Version 9 (including 9(32)) from 09-00 through 09-66-22, HiRDB Server with Additional Function Version 9 through 09-66/V, and HiRDB Server Version 10 before 10-11-02. To check a installation, compare its HiRDB version against these ranges.
¿Qué hacer?For Version 10, move to 10-11-02 or later, which is the fixed release in the listed range. The facts give no fixed release for Version 9 builds, so check Hitachi's advisory for that line.
Descripción original del registro (Hitachi)

Authentication Bypass by Spoofing Vulnerability in HiRDB. This issue affects HiRDB Server Version 10: from 10-00 before 10-12-01; HiRDB Server Version 9: from 09-00 through 09-66-22; HiRDB Server with Additional Function Version 9: from 09-00 through 09-66/V; HiRDB Server Version 9(32): from 09-02 through 09-66-22; HiRDB Server with Additional Function Version 9(32): from 09-00 through 09-66-/V.

Contexto

Condiciones y alcance

Condiciones necesarias para que el fallo sea explotable
01
Affects the HiRDB Server and HiRDB Server with Additional Function versions listed by the vendor, across AIX, HP-UX, Linux, Solaris and Windows builds.“Affected products and versions are listed below.”
Vector CVSS 3.1

Desglose de métricas

Opción resaltada = valor del vector · izquierda = peor caso · CNA
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:L
BajaAlta
PrivilegiosPR:N
NingunoBajosAltos
InteracciónUI:N
NingunaRequerida
AlcanceS:U
CambiadoSin cambio
ConfidencialidadC:H
AltoBajoNinguno
IntegridadI:H
AltoBajoNinguno
DisponibilidadA:H
AltoBajoNinguno
Versiones

Rangos afectados

Afectada Corregida
HiRDB Server Version 9≥ 09-00 ≤ 09-66-22
HiRDB Server with Additional Function Version 9≥ 09-00 ≤ 09-66/V
HiRDB Server with Additional Function Version 9(32)≥ 09-00 ≤ 09-66-/V
HiRDB Server Version 9(32)≥ 09-02 ≤ 09-66-22
HiRDB Server Version 10≥ 10-00 < 10-11-02
09-66/V
09-00
09-02
09-66-/V
09-66-22
10-00
10-11-02
Remediación

Estado del parche por paquete

Paquete / productoEstadoCorregida enDesde divulgaciónÚltima versión
HiRDB Server
Corregida 10-11-02 — —
Versiones corregidas10-11-02
Explotación

Arsenal público

Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.

Registro
EscenarioGENERALHitachi
Referencias
Fabricantehttps://www.hitachi.com/products/it/software/security/info/vuls/hitachi-sec-2026-149/index.html

Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.