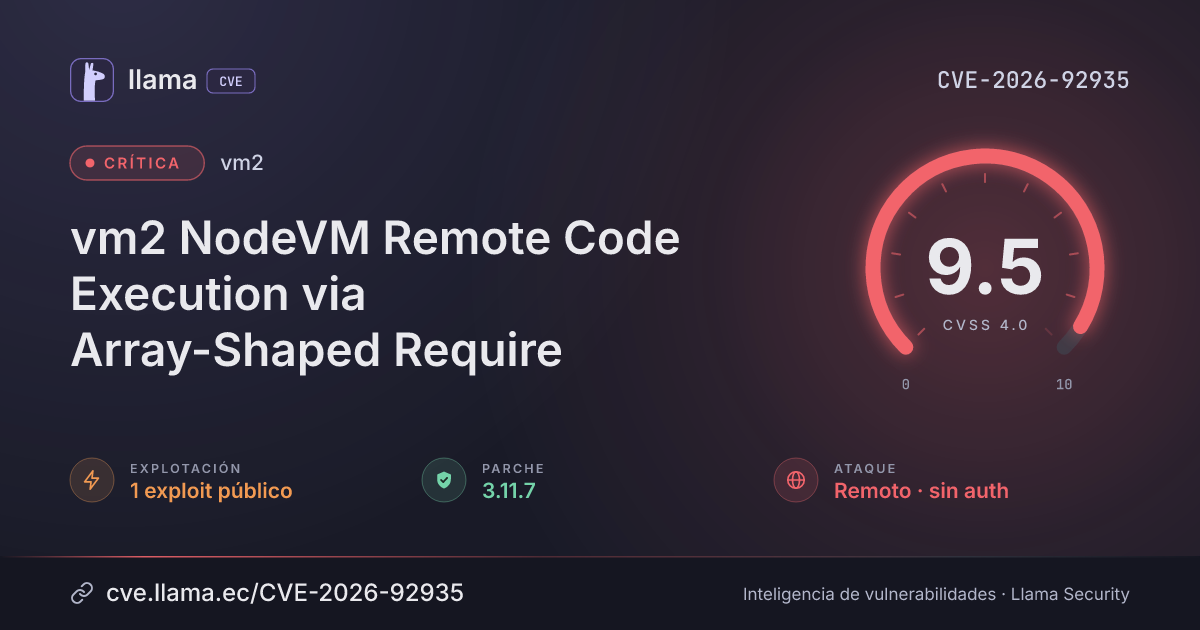
CVE-2026-92935
vm2 NodeVM Remote Code Execution via Array-Shaped Require
CVSS:4.0/AV:N/AC:H/AT:P/PR:N/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 3.11.7 | vm2 · -24 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-92935 divulgada · CVSS 9.5 (CNA) | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice |
vm2 is a sandbox for running untrusted Node.js code. In versions >= 3.11.4 and <= 3.11.6, the NodeVM constructor computes `hasRealRequireConfig` with `typeof requireOpts === 'object' && requireOpts !== null`, so an array-shaped `require` value (for example `require: []`) satisfies the guard that is meant to reject nesting without an explicit require configuration. `makeResolverFromLegacyOptions()` then destructures the array into undefined option fields and returns a resolver containing only `NESTING_OVERRIDE.vm2`. As a result, an attacker who can supply JavaScript executed by a NodeVM configured with truthy `nesting` and an array-shaped `require` (e.g. `new NodeVM({nesting: true, require: []})`) can require the host `vm2` module, create an inner NodeVM with an attacker-chosen builtin allowlist (such as `child_process`), and execute arbitrary commands with the privileges of the host Node.js process, escaping the sandbox. Outer builtin restrictions do not constrain the attacker-created inner NodeVM. This issue is fixed in vm2 3.11.7.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
npmvm2 |
Corregida | 3.11.7 | -24 d | 3.12.2 no afectada |
3.11.7Arsenal público
Ver los 1 repositorios de GitHub
Los repositorios públicos incluyen exploits, escáneres, laboratorios y reglas de detección. No ejecute código de terceros sin revisarlo en un entorno aislado.
https://github.com/patriksimek/vm2/security/advisories/GHSA-8hr7-r645-pc6whttps://github.com/patriksimek/vm2/commit/54b54b74a382577f0bcd0538c5bf99acdcd7f53bhttps://github.com/CompleteTech-Security/vm2-nesting-checkhttps://www.vulncheck.com/advisories/vm2-nodevm-remote-code-execution-via-array-shaped-requireLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.