llamaCVEVulnerability Intelligence
/
Octopus Server

CVE-2026-93487

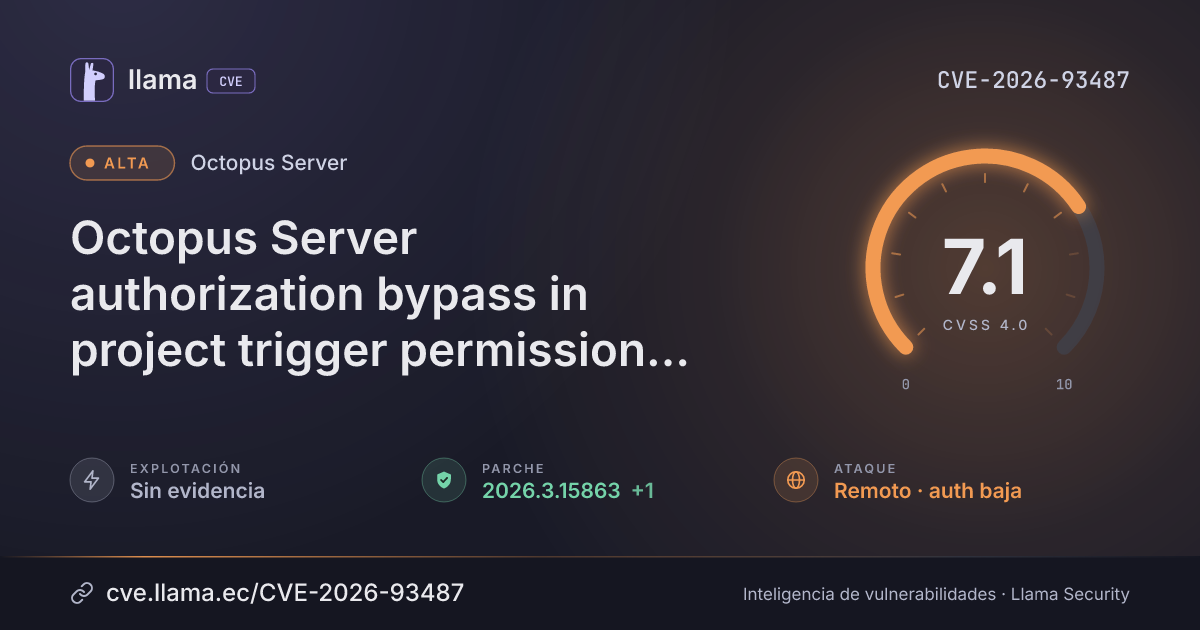
Octopus Server authorization bypass in project trigger permission checks

A low-privileged user on the network can run runbooks and create deployments they are not authorised to perform.

Specific setups onlyParche disponibleauthorization bypass
Descargar PNG JSON
CVSS 4.0
7.1
Alta
CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:N/VC:N/VI:H/VA:L/SC:N/SI:N/SA:N Fuente: CNA
ExplotaciónSin evidenciaSSVC: none · no figura en CISA KEV
Exploits públicos0Ninguno conocido
Parche2 versiones2026.2.13487 · 2026.3.15863
Exposición8 dDesde la divulgación, 11 nov 2026, 2:21 a. m.
Detección7 minDesde la divulgación hasta su ingreso al índice
Decisión SSVCSeguir
Remediar en la ventana regular de mantenimiento
Sin explotación conocida, no automatizable e impacto técnico parcial. Hay versiones corregidas disponibles.
Timeline

Ciclo de vida de la vulnerabilidad

Hoy
Divulgación
Publicada
Evaluación SSVC +1
Explotación
Remediación
Monitoreo
Detectada +2
Verificada
11 nov 26
16 nov 26
19 nov 26
11 nov 26
13 nov 26
15 nov 26
17 nov 26
19 nov 26
FechaFaseEventoDetalle
Divulgación Publicada CVE-2026-93487 divulgada · CVSS 7.1 (CNA)
Monitoreo Detectada Ingresó al índice
Monitoreo Fuente: NIST NVD Registro visto por primera vez en NIST NVD
Monitoreo Fuente: ENISA EUVD Registro visto por primera vez en ENISA EUVD
Divulgación Evaluación SSVC CISA-ADP · explotación ninguna
Divulgación Modificada Última actualización del registro
Monitoreo Verificada Última verificación contra las fuentes
Resumen
Resumen generado por IA · CC-BY 4.0 · 11 nov 2026

Octopus Server, from Octopus Deploy, has a flaw in how it checks permissions for users who can create project triggers. A user with low-level login access over the network could run runbooks or create deployments they are not authorised to perform.

Affects Octopus Server from 2019.11.0 up to the fixed releases, including 2020.x through 2025.x. Fixed in 2026.2.13487 and 2026.3.15863.

¿Qué significa?Octopus Server does not correctly validate the permissions assigned to a user. As a result, a user can run runbooks or create deployments they are not authorised to perform.
¿Quién está afectado?Octopus Server 2020.x through 2025.x, 2019.x releases after 2019.11, and 2026.x before 2026.2.13487 or 2026.3 before 2026.3.15863 are affected. Check the installed Octopus Server version to see whether it falls in these ranges.
¿Qué hacer?Upgrade to Octopus Server 2026.2.13487 or later, or to 2026.3.15863 or later if you are on the 2026.3 line.
Descripción original del registro (Octopus)

In affected versions of Octopus Server, incorrect validation of the permissions assigned to a user that would allow them to create project triggers could result in the user being able to run runbooks or create deployments they were not authorised to perform.

Contexto

Condiciones y alcance

Condiciones necesarias para que el fallo sea explotable
01
Octopus Server running an affected version: all 2020.x through 2025.x, 2019.x after 2019.11.x, and 2026.x before 2026.2.13487 or 2026.3 before 2026.3.15863.“All 2020.x, 2021.x, 2022.x, 2023.x 2024.x and 2025.x versions”
¿Quién debe revisar?Teams running Octopus Server 2019.11 or later, including 2020-2025 builds and 2026 builds before 2026.2.13487 or 2026.3.15863.
Vector CVSS 4.0

Desglose de métricas

Opción resaltada = valor del vector · izquierda = peor caso · CNA
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:L
BajaAlta
Requisitos de ataqueAT:N
NingunoPresentes
PrivilegiosPR:L
NingunoBajosAltos
InteracciónUI:N
NingunaPasivaActiva
Confid. (sistema)VC:N
AltoBajoNinguno
Integridad (sistema)VI:H
AltoBajoNinguno
Disponib. (sistema)VA:L
AltoBajoNinguno
Confid. (posterior)SC:N
AltoBajoNinguno
Integridad (posterior)SI:N
AltoBajoNinguno
Disponib. (posterior)SA:N
AltoBajoNinguno
Versiones

Rangos afectados

Afectada Corregida
Octopus Server≥ 2019.11.0 < 2026.2.13487
Octopus Server≥ 2026.3.0 < 2026.3.15863
2019.11.0
2026.2.13487
2026.3.0
2026.3.15863
Remediación

Estado del parche por paquete

Paquete / productoEstadoCorregida enDesde divulgaciónÚltima versión
Octopus Server
Corregida 2026.2.13487, 2026.3.15863 — —
Versiones corregidas2026.2.134872026.3.15863
Explotación

Arsenal público

Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.

Registro
EscenarioGENERALOctopus
Referencias
Fabricantehttps://advisories.octopus.com/post/2026/sa2026-20

Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.