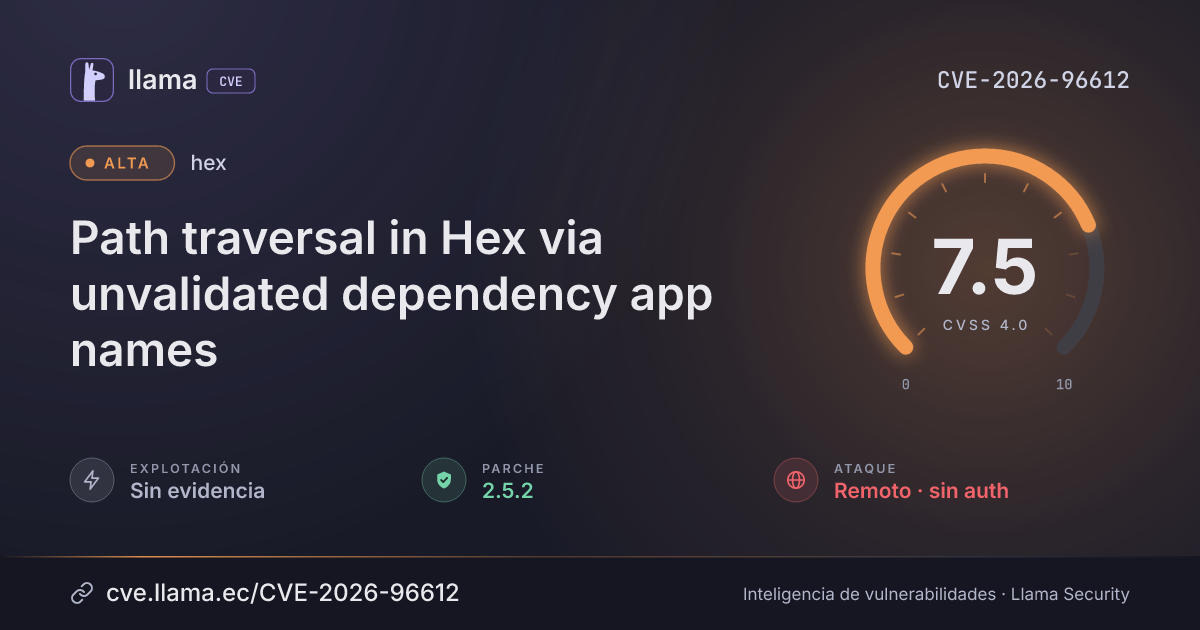
ExplotaciónSin evidenciaSSVC: none · no figura en CISA KEV
Exploits públicos0Ninguno conocido
Parche1 versión2.5.2
Exposición37 dDesde la divulgación, 12 oct 2026, 10:39 a. m.
Detección10 dDesde la divulgación hasta su ingreso al índice
Decisión SSVCSeguir de cerca
Monitorear y programar la remediación
Sin explotación conocida, no automatizable e impacto técnico total. Hay versiones corregidas disponibles.
Timeline
Ciclo de vida de la vulnerabilidad
Hoy
Divulgación
Publicada
Evaluación SSVC
Modificada
Explotación
Remediación
Monitoreo
Detectada
Fuente: OSV
Fuente: NIST NVD
Verificada
12 oct 26
16 oct 26
22 oct 26
24 oct 26
11 nov 26
19 nov 26
12 oct 26
22 oct 26
31 oct 26
10 nov 26
19 nov 26
Fecha
Fase
Evento
Detalle
Divulgación
Publicada
CVE-2026-96612 divulgada · CVSS 7.5 (CNA)
Divulgación
Evaluación SSVC
CISA-ADP · explotación ninguna
Monitoreo
Detectada
Ingresó al índice
Monitoreo
Fuente: OSV
Registro visto por primera vez en OSV
Monitoreo
Fuente: NIST NVD
Registro visto por primera vez en NIST NVD
Divulgación
Modificada
Última actualización del registro
Monitoreo
Verificada
Última verificación contra las fuentes
Resumen
Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal') vulnerability in hexpm hex allows a malicious package publisher to delete a directory outside the project's deps directory and extract package files into it when a developer fetches dependencies.
A package release's requirements carry an app label that names the dependency's OTP application. Hex takes this label from the repository's signed registry and uses it as the dependency's application name without validating it (Hex.RemoteConverger.deps/2, Hex.Mix.to_lock/1). Mix derives the dependency's checkout directory as deps/<app>, and Hex.SCM.update/1 runs File.rm_rf!/1 on that directory and unpacks the package into it. hex.pm only checks the label's length, so a publisher can set it to a value such as ../../target. When a project depends on such a release directly or transitively, mix deps.get or mix deps.update deletes the directory the label resolves to and writes the labelled package's files there. This happens before any dependency code is compiled.
This issue affects hex: from 0.6.0 before 2.5.2.
Affects Hex from 0.6.0 before 2.5.2 when dependencies are fetched with mix deps.get or mix deps.update and the tree includes a crafted package release. Fixed in Hex 2.5.2.
¿Qué significa?A malicious package publisher can make mix deps.get delete a directory outside the project's deps directory and fill it with attacker-chosen package files. Those files can lead to code execution without the developer compiling the dependency.
¿Quién está afectado?Hex versions from 0.6.0 before 2.5.2 are affected. Projects are affected when their dependency tree, directly or transitively, contains a package release whose registry metadata carries a crafted dependency app label, and dependencies are fetched with mix deps.get or mix deps.update. Packages on self-hosted repositories are affected when the repository operator signs such metadata. To check, look at the installed Hex version and at the dependency tree for such a release.
¿Qué hacer?Upgrade Hex to 2.5.2 or later, for example with mix local.hex. The vendor's patch ids for this issue are 1b3e2ae and 72279a8.
Contexto
Condiciones y alcance
Condiciones necesarias para que el fallo sea explotable
01
Project depends directly or transitively on a package release whose registry metadata carries a crafted dependency app label.“Affects projects whose dependency tree, directly or transitively, contains a package release whose registry metadata carries a crafted dependency app label”
02
Dependencies are fetched with mix deps.get or mix deps.update.“when dependencies are fetched with mix deps.get or mix deps.update”
03
Hex versions from 0.6.0 before 2.5.2.“This issue affects hex: from 0.6.0 before 2.5.2.”
04
Packages on self-hosted repositories are affected when the repository operator signs such metadata.“packages on self-hosted repositories are affected when the repository operator signs such metadata.”
MitigaciónBefore running mix deps.get on a mix.lock from an untrusted change, check that every key in mix.lock is a plain application name without / , \ or .. .
Vector CVSS 4.0
Desglose de métricas
Opción resaltada = valor del vector · izquierda = peor caso · CNA
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:L
BajaAlta
Requisitos de ataqueAT:P
NingunoPresentes
PrivilegiosPR:N
NingunoBajosAltos
InteracciónUI:A
NingunaPasivaActiva
Confid. (sistema)VC:H
AltoBajoNinguno
Integridad (sistema)VI:H
AltoBajoNinguno
Disponib. (sistema)VA:H
AltoBajoNinguno
Confid. (posterior)SC:N
AltoBajoNinguno
Integridad (posterior)SI:N
AltoBajoNinguno
Disponib. (posterior)SA:N
AltoBajoNinguno
Versiones
Rangos afectados
AfectadaCorregida
hex≥ 0.6.0 < 2.5.2
0.6.0
2.5.2
Remediación
Estado del parche por paquete
Paquete / producto
Estado
Corregida en
Desde divulgación
Última versión
hex
Corregida
2.5.2
—
—
Versiones corregidas2.5.2
Explotación
Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
Registro
EscenarioGENERALEEF
configurationAffects projects whose dependency tree, directly or transitively, contains a package release whose registry metadata carries a crafted dependency app label, when dependencies are fetched with mix deps.get or mix deps.update. Packages on hex.pm are affected while hex.pm accepts such labels; packages on self-hosted repositories are affected when the repository operator signs such metadata.EEF
MitigaciónBefore running mix deps.get on a mix.lock from an untrusted change, check that every key in mix.lock is a plain application name without /, \ or ... There's no workaround for new dependency resolution with mix deps.update or mix deps.get without a lock entry.EEF
solutionUpgrade Hex to 2.5.2 or later, for example with mix local.hex. Hex then skips package releases that give a dependency an application name other than a letter followed by letters, digits, _ and -, and warns about them. Resolution fails if no other release of the package fits the requirements.EEF
Usamos cookies propias estrictamente necesarias para que el sitio funcione y sea seguro. Con tu permiso, también usamos almacenamiento local para recordar tus preferencias y medir el uso del sitio de forma agregada. Puedes aceptar, rechazar o configurar cada categoría, y cambiar tu decisión cuando quieras desde el enlace “Preferencias de cookies” del pie de página. Más información
Preferencias de cookies
Elige qué permites
Solo usamos tecnologías propias de este dominio. Sin publicidad ni rastreadores de terceros. Detalle en la Política de cookies.