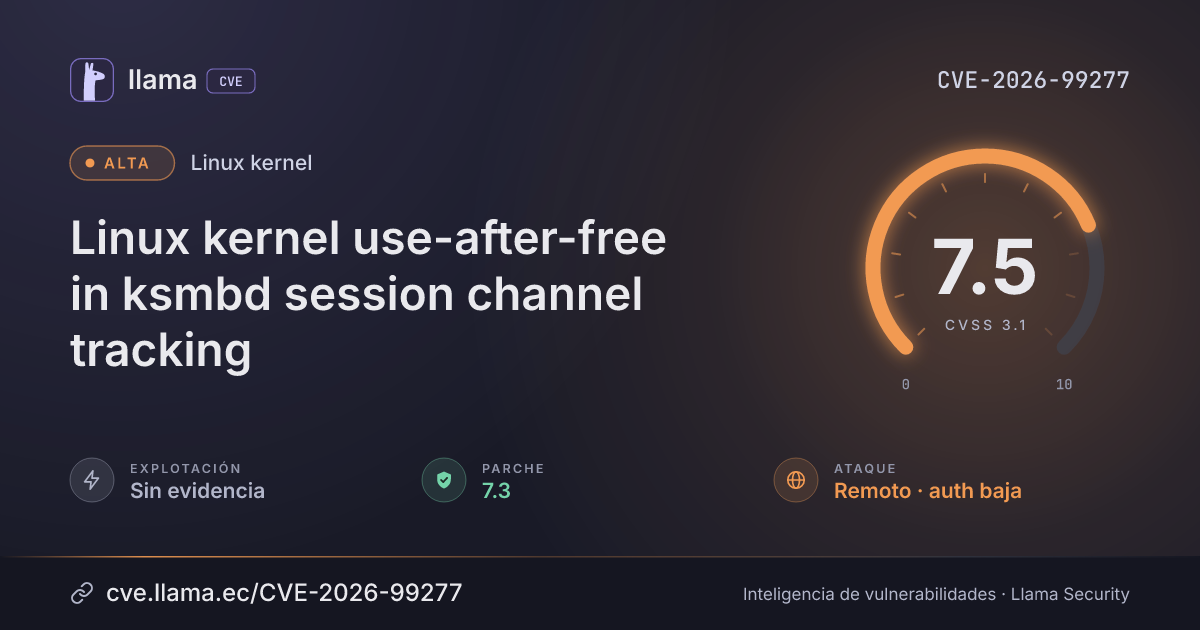
CVE-2026-99277
Linux kernel use-after-free in ksmbd session channel tracking
Freed connections can still be used in session handling, but what an attacker could gain is not yet known.
CVSS:3.1/AV:N/AC:H/PR:L/UI:N/S:U/C:H/I:H/A:H
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-99277 divulgada · CVSS 7.5 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Fuente: OSV | Registro visto por primera vez en OSV | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
The Linux kernel's ksmbd SMB server has a use-after-free flaw in how it tracks session channels: a connection can be freed while another session reference is still using it. The provided data does not state what an attacker can gain or how they would reach the flaw, so no attack vector can be described.
Descripción original del registro (Linux)
In the Linux kernel, the following vulnerability has been resolved: ksmbd: hold a connection reference for each session channel ksmbd_session_unregister() removes a session from the global and per- connection tables before dropping the table reference. A concurrent reference holder can keep the session and its channel list alive after those removals. Connection cleanup can no longer find the unpublished session to remove its channels. Since a channel only stores a raw conn pointer, the connection can be freed while another session reference holder is still accessing it, for example during SMB3.1.1 binding or a procfs read. Take a connection reference when registering a channel and release it on insertion failure, channel removal, or final session destruction. Keep the channels and signing keys until the session is destroyed so a response can still be signed after the session has been unregistered.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
Linux |
Corregida | 7.3 | — | — |
7.3Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://git.kernel.org/stable/c/4b333aed69cfc2c8687b86b6a4364a0dffc16dd8https://git.kernel.org/stable/c/add8d7fb04efe564193df73581889c62fc0016f1Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.