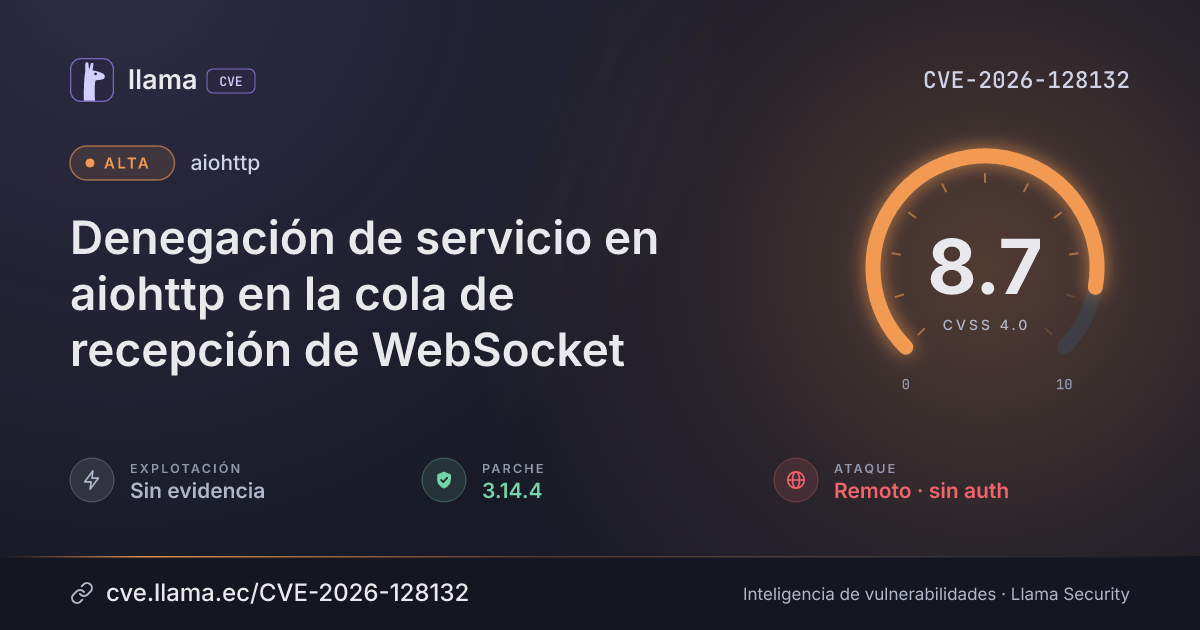
CVE-2026-128132
aiohttp denial of service in WebSocket receive queue
A remote peer can send many small or compressed WebSocket messages to exhaust memory on a server or client.
Texto original en inglés · Ver en español
CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:N/VI:N/VA:H/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 3.14.4 | aiohttp · -39 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-128132 divulgada · CVSS 8.7 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Fuente: ENISA EUVD | Registro visto por primera vez en ENISA EUVD | |
| Monitoreo | Fuente: OSV | Registro visto por primera vez en OSV | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
AIOHTTP is an asynchronous HTTP client/server framework for asyncio and Python. Prior to 3.14.4, the WebSocket reader continues parsing frames already received after the receive queue pauses the transport, and empty messages are not counted toward the queue size. With permessage-deflate, one read of compressed frames can add many megabytes of decompressed messages to the receive queue. A remote peer can send many small or compressed messages faster than the application consumes them and cause excessive memory use in a server or client. This issue is fixed in version 3.14.4.
Affects aiohttp 3.14.3 and earlier WebSocket servers and clients, where small or compressed messages can bypass the receive queue limits. Fixed in 3.14.4.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
pypiaiohttp |
Corregida | 3.14.4 | -39 d | 3.14.5 no afectada |
3.14.4Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/aio-libs/aiohttp/security/advisories/GHSA-5rmc-48h2-hvcmhttps://github.com/aio-libs/aiohttp/pull/13393https://github.com/aio-libs/aiohttp/pull/13545https://github.com/aio-libs/aiohttp/pull/13546https://github.com/aio-libs/aiohttp/commit/0ae507423f681161efa77d20052b4054397c7fb6https://github.com/aio-libs/aiohttp/commit/5e54037933fa8422be5fa8a2002d118ed2d4e5e0https://github.com/aio-libs/aiohttp/commit/b62321b6fa264a89f4aca084ad60fc38a59ffa51https://github.com/aio-libs/aiohttp/releases/tag/v3.14.4Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.