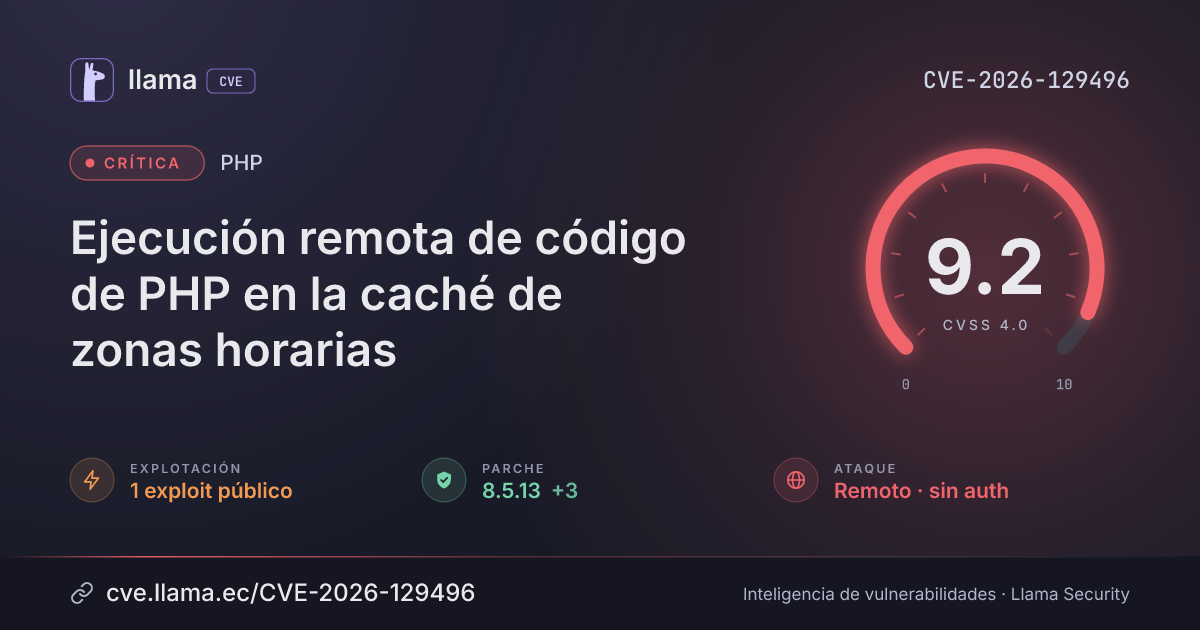
CVE-2026-129496
PHP remote code execution in timezone cache
A remote attacker without logging in can crash worker processes with a crafted request and may run arbitrary code.
Texto original en inglés · Ver en español
CVSS:4.0/AV:N/AC:H/AT:P/PR:N/UI:N/VC:H/VI:H/VA:H/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Publicada | CVE-2026-129496 divulgada · CVSS 9.2 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Fuente: ENISA EUVD | Registro visto por primera vez en ENISA EUVD | |
| Explotación | Exploit en GitHub | abraxas/php-tzcache-rce | |
| Monitoreo | Fuente: PoC-in-GitHub | Registro visto por primera vez en PoC-in-GitHub | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
A use-after-free bug in the timezone cache of PHP (from the PHP Group), in non-thread-safe builds where a startup warning is written to a file-based error log, lets an attacker crash PHP-FPM, Apache mod_php or CGI workers. Arbitrary code execution may also be possible. The attacker can reach it remotely, without logging in, by sending a crafted request.
Affects PHP before 8.2.36, 8.3.x before 8.3.37, 8.4.x before 8.4.28 and 8.5.x before 8.5.13, when diagnostics go to a file-based error_log. Fixed in those versions.
Descripción original del registro (php)
Timezone cache use-after-free can lead to remote code execution. In non-thread-safe builds, a diagnostic written to a file-based error_log during module startup, for example for an invalid date.timezone value or a session configuration warning, causes the timezone cache to be allocated in startup memory that is freed while a reference to it is kept. A diagnostic raised early in the first request of a worker, such as the max_input_vars warning, then accesses the freed cache. On such a deployment an unauthenticated remote attacker can crash PHP-FPM, Apache mod_php or CGI workers with a crafted request. Arbitrary code execution may be possible and has been demonstrated with known memory addresses. This issue affects PHP versions before 8.2.36, 8.3.* before 8.3.37, 8.4.* before 8.4.28 and 8.5.* before 8.5.13.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
PHP |
Corregida | 8.2.36, 8.3.37, 8.4.28, 8.5.13 | — | — |
8.2.368.3.378.4.288.5.13Arsenal público
Ver los 1 repositorios de GitHub (1 con exploit confirmado)
Los repositorios públicos incluyen exploits, escáneres, laboratorios y reglas de detección. No ejecute código de terceros sin revisarlo en un entorno aislado.
https://github.com/php/php-src/security/advisories/GHSA-gr4f-wgx5-jpfvhttps://github.com/abraxas/php-tzcache-rceLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.