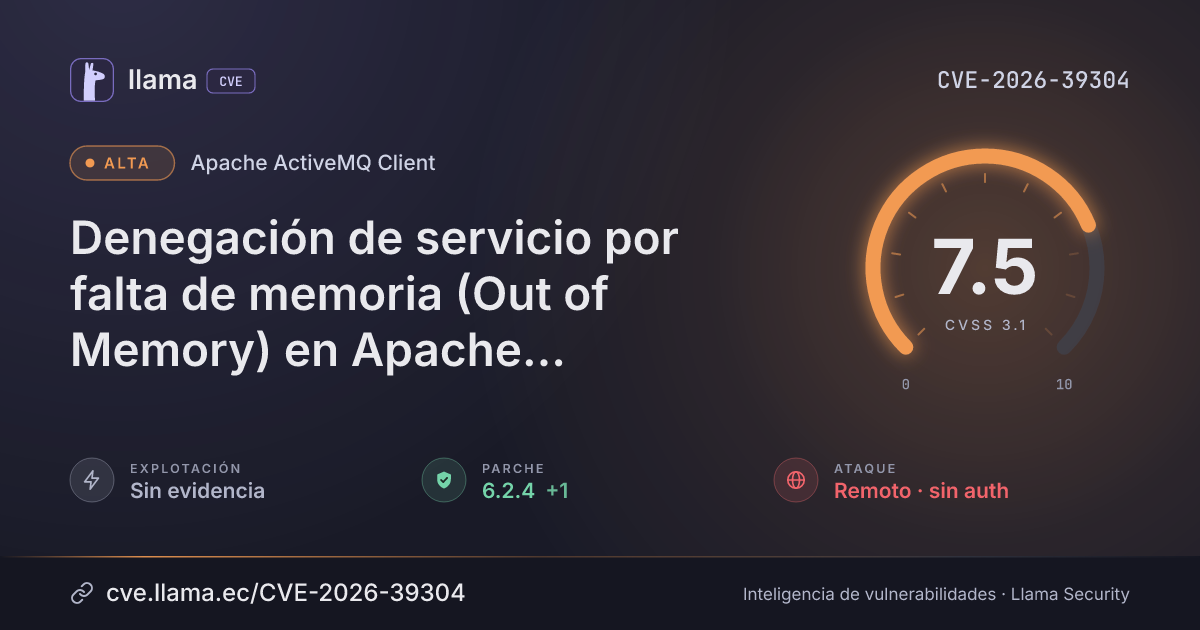
CVE-2026-39304
Denial of Service via Out of Memory vulnerability in Apache ActiveMQ Client, Apache ActiveMQ Broker, Apache ActiveMQ
Texto original en inglés · Ver en español
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H
Fuente: CISA-ADP
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:HCiclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 5.19.4 | org.apache.activemq:activemq-client · -13 d desde divulgación | |
| Remediación | Parche 6.2.4 | org.apache.activemq:activemq-client · -2 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-39304 divulgada · CVSS 7.5 (CISA-ADP) | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Detectada | Ingresó al índice |
Denial of Service via Out of Memory vulnerability in Apache ActiveMQ Client, Apache ActiveMQ Broker, Apache ActiveMQ. ActiveMQ NIO SSL transports do not correctly handle TLSv1.3 handshake KeyUpdates triggered by clients. This makes it possible for a client to rapidly trigger updates which causes the broker to exhaust all its memory in the SSL engine leading to DoS. Note: TLS versions before TLSv1.3 (such as TLSv1.2) are broken but are not vulnerable to OOM. Previous TLS versions require a full handshake renegotiation which causes a connection to hang but not OOM. This is fixed as well. This issue affects Apache ActiveMQ Client: before 5.19.4, from 6.0.0 before 6.2.4; Apache ActiveMQ Broker: before 5.19.4, from 6.0.0 before 6.2.4; Apache ActiveMQ: before 5.19.4, from 6.0.0 before 6.2.4. Users are recommended to upgrade to version 6.2.4 or 5.19.5, which fixes the issue.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
mavenorg.apache.activemq:activemq-client |
Corregida | 5.19.4, 6.2.4 | -13 d · -2 d | 6.4.0 no afectada |
mavenorg.apache.activemq:activemq-broker |
Corregida | 5.19.4, 6.2.4 | -13 d · -2 d | 6.4.0 no afectada |
mavenorg.apache.activemq:activemq-all |
Corregida | 5.19.4, 6.2.4 | -13 d · -2 d | 6.4.0 no afectada |
mavenorg.apache.activemq:apache-activemq |
Corregida | 5.19.4, 6.2.4 | -13 d · -2 d | 6.4.0 no afectada |
5.19.46.2.4Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://activemq.apache.org/security-advisories.data/CVE-2026-39304-announcement.txthttp://www.openwall.com/lists/oss-security/2026/04/09/17https://bugzilla.redhat.com/show_bug.cgi?id=2457275https://access.redhat.com/security/cve/CVE-2026-39304https://security.access.redhat.com/data/csaf/v2/vex/2026/cve-2026-39304.jsonLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.