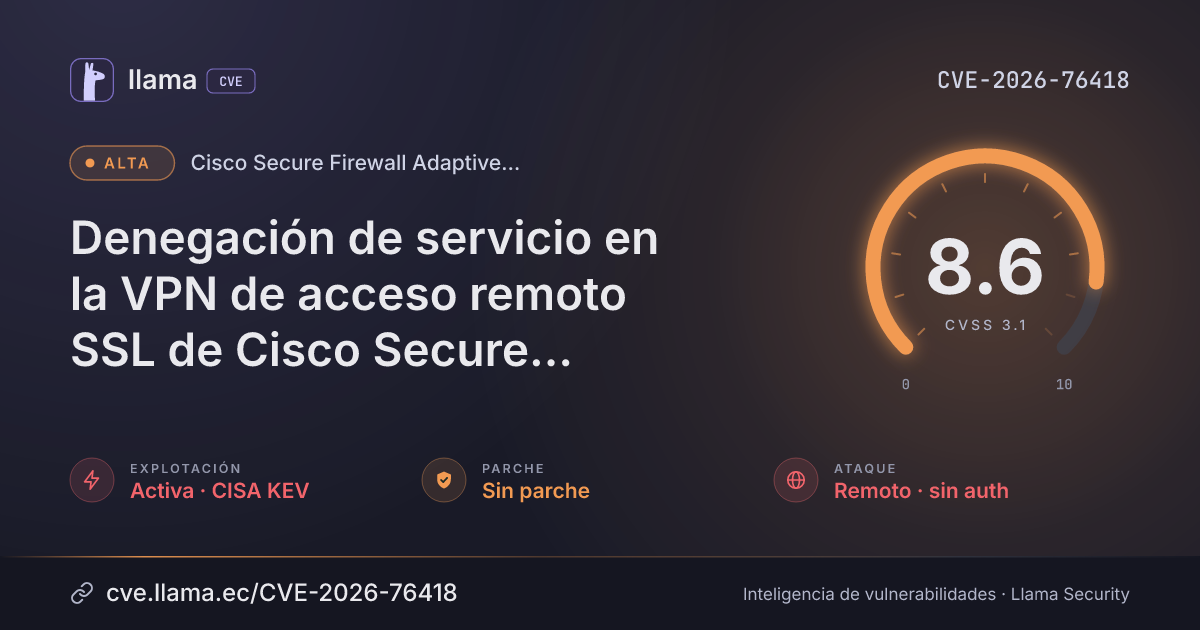
CVE-2026-76418
Cisco Secure Firewall Adaptive Security Appliance (ASA) Software denial of service in SSL remote access VPN
An unauthenticated attacker can make the device reload by sending a crafted request to its SSL VPN.
Texto original en inglés · Ver en español
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:N/I:N/A:H
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Evaluación SSVC | CISA-ADP · explotación activa | |
| Divulgación | Publicada | CVE-2026-76418 divulgada · CVSS 8.6 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Fuente: ENISA EUVD | Registro visto por primera vez en ENISA EUVD | |
| Explotación | CISA KEV | Agregada al catálogo de vulnerabilidades explotadas | |
| Divulgación | Modificada | Última actualización del registro | |
| Remediación | Plazo KEV | Fecha límite de remediación para agencias federales (EE. UU.) | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Cisco Secure Firewall ASA Software and Secure Firewall Threat Defense Software let an attacker make the device reload unexpectedly, causing a denial of service, by sending a crafted request to the SSL remote access VPN remotely and without logging in. The bug needs a non-default setup (secondary authentication configured on a tunnel group), and CISA lists it as actively exploited in attacks.
Affects Cisco Secure Firewall ASA and FTD Software with the SSL remote access VPN login service reachable and secondary authentication set in a tunnel group. Cisco has released software updates.
Descripción original del registro (cisco)
A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software and Cisco Secure Firewall Threat Defense (FTD) Software could allow an unauthenticated, remote attacker to cause the device to reload unexpectedly, resulting in a denial of service (DoS) condition. This vulnerability is due to logic errors when secondary authentication is configured on a tunnel group. An attacker could exploit this vulnerability by sending a crafted request when connecting to the SSL remote access VPN. A successful exploit could allow the attacker to cause the affected device to reload, resulting in a DoS condition.
Condiciones y alcance
Desglose de métricas
Versiones afectadas
9.16.19.16.1.289.16.29.16.2.39.16.2.79.16.2.119.16.2.139.16.2.149.16.3.39.16.39.16.3.149.18.19.16.3.159.18.1.39.18.29.16.3.199.16.3.239.18.2.59.16.49.18.2.79.19.19.16.4.99.18.2.89.16.4.149.18.39.19.1.59.16.4.189.19.1.99.18.3.399.16.4.199.19.1.129.18.3.469.16.4.279.19.1.189.18.3.539.18.3.559.16.4.389.16.4.399.18.3.569.20.19.16.4.429.19.1.229.18.49.20.1.59.18.4.59.19.1.249.16.4.489.18.4.89.20.29.19.1.279.16.4.559.18.4.229.20.2.109.16.4.579.19.1.289.18.4.249.20.2.219.16.4.619.19.1.319.18.4.29Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
Cisco Secure Firewall Adaptive Security Appliance (ASA) Software |
Sin parche | — | — | — |
Cisco Secure Firewall Threat Defense (FTD) Software |
Sin parche | — | — | — |
Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-asaftd-tunnel-dos-s6mgkb75https://www.cisa.gov/known-exploited-vulnerabilities-catalog?field_cve=CVE-2026-76418Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.