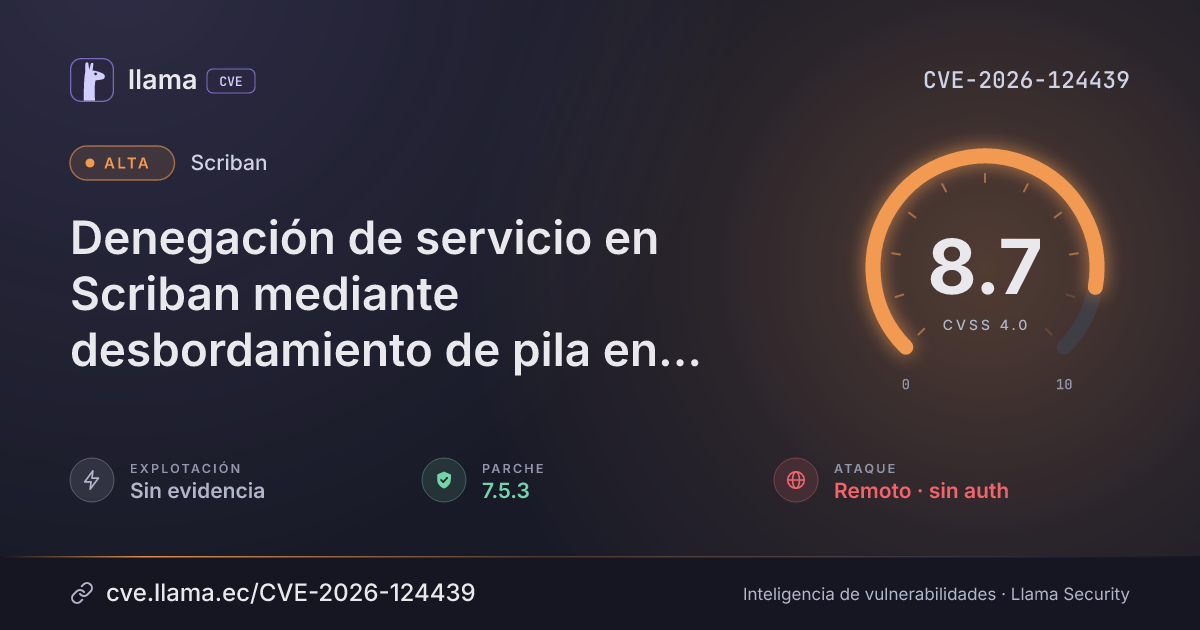
CVE-2026-124439
Scriban denial of service via stack overflow in template engine
A remote attacker who can supply a template can crash the entire host process without logging in.
CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:N/VI:N/VA:H/SC:N/SI:N/SA:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Remediación | Parche 7.5.3 | Scriban · -15 d desde divulgación | |
| Divulgación | Publicada | CVE-2026-124439 divulgada · CVSS 8.7 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Fuente: ENISA EUVD | Registro visto por primera vez en ENISA EUVD | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Fuente: OSV | Registro visto por primera vez en OSV | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
Scriban (and Scriban.Signed) before 7.5.3 can be crashed remotely, without logging in, by an attacker who can supply a template, because several recursion paths skip the library's depth limits. A successful attack terminates the host process entirely, causing a denial of service.
Scriban and Scriban.Signed 7.5.2 and older are affected when a host renders or parses attacker-supplied templates, even with default settings. Fixed in 7.5.3.
Descripción original del registro (VulnCheck)
Scriban and Scriban.Signed before 7.5.3 contain uncontrolled recursion flaws in which postfix member, indexer, and call chains bypass ExpressionDepthLimit, array comparison lacks depth and cycle checks, and object.eval bypasses RecursiveLimit. Attackers who can supply templates can trigger an uncatchable StackOverflowException that terminates the host process.
Condiciones y alcance
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
nugetScriban |
Corregida | 7.5.3 | -15 d | 7.6.1 no afectada |
nugetScriban.Signed |
Corregida | 7.5.3 | -15 d | 7.6.1 no afectada |
7.5.3Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/scriban/scriban/security/advisories/GHSA-mvmw-9jxc-7pr2https://www.vulncheck.com/advisories/scriban-before-7.5.3-denial-of-service-via-uncatchable-stackoverflowexceptionLas referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.