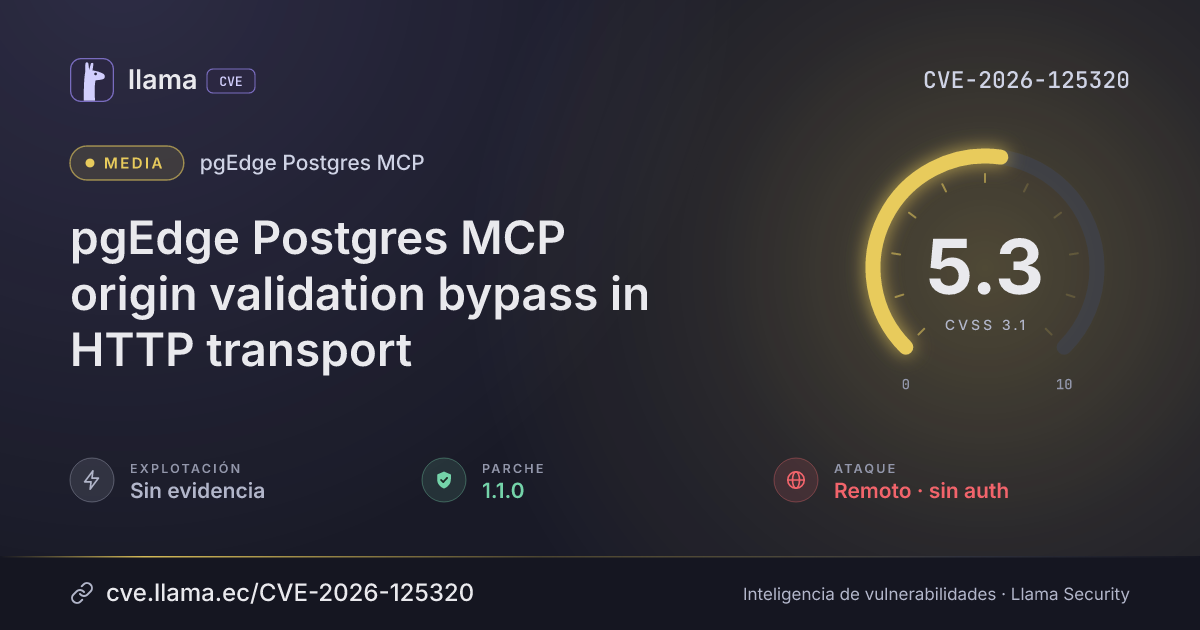
CVE-2026-125320
pgEdge Postgres MCP origin validation bypass in HTTP transport
Remote attackers can read database schemas and query results without logging in, via DNS rebinding on a malicious page.
CVSS:3.1/AV:N/AC:H/PR:N/UI:R/S:U/C:H/I:N/A:N
Fuente: CNA
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-125320 divulgada · CVSS 5.3 (CNA) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Fuente: ENISA EUVD | Registro visto por primera vez en ENISA EUVD | |
| Monitoreo | Fuente: OSV | Registro visto por primera vez en OSV | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
The pgEdge Postgres MCP Server, which runs SQL queries against PostgreSQL databases through MCP-compatible clients, did not validate the Origin header on its HTTP transport. A remote attacker can exploit this without logging in by luring a user to a malicious page using DNS rebinding, which can read database schemas and query results, but only when the HTTP transport is enabled on a machine that also runs a browser.
Descripción original del registro (GitHub_M)
pgEdge Postgres MCP Server enables SQL queries against PostgreSQL databases through Model Context Protocol compatible clients. Prior to 1.1.0, the HTTP transport did not validate the Origin header on incoming requests. A user who visited an attacker-controlled page could be targeted through DNS rebinding, allowing the page to reach a locally running server and read schemas and query results from configured databases. The issue affected deployments with the HTTP transport enabled on a machine that also ran a browser, while the default stdio transport was not reachable through this path. This issue is fixed in version 1.1.0.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
pgedge-postgres-mcp |
Corregida | 1.1.0 | — | — |
1.1.0Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://github.com/pgEdge/pgedge-postgres-mcp/security/advisories/GHSA-6hg5-9f3w-c886https://github.com/pgEdge/pgedge-postgres-mcp/issues/231https://github.com/pgEdge/pgedge-postgres-mcp/pull/232https://github.com/pgEdge/pgedge-postgres-mcp/commit/5571bd492a803e8f8831599c88b4619c5041fd8ehttps://github.com/pgEdge/pgedge-postgres-mcp/releases/tag/v1.1.0Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.