llamaCVEVulnerability Intelligence
/
ExcelJS

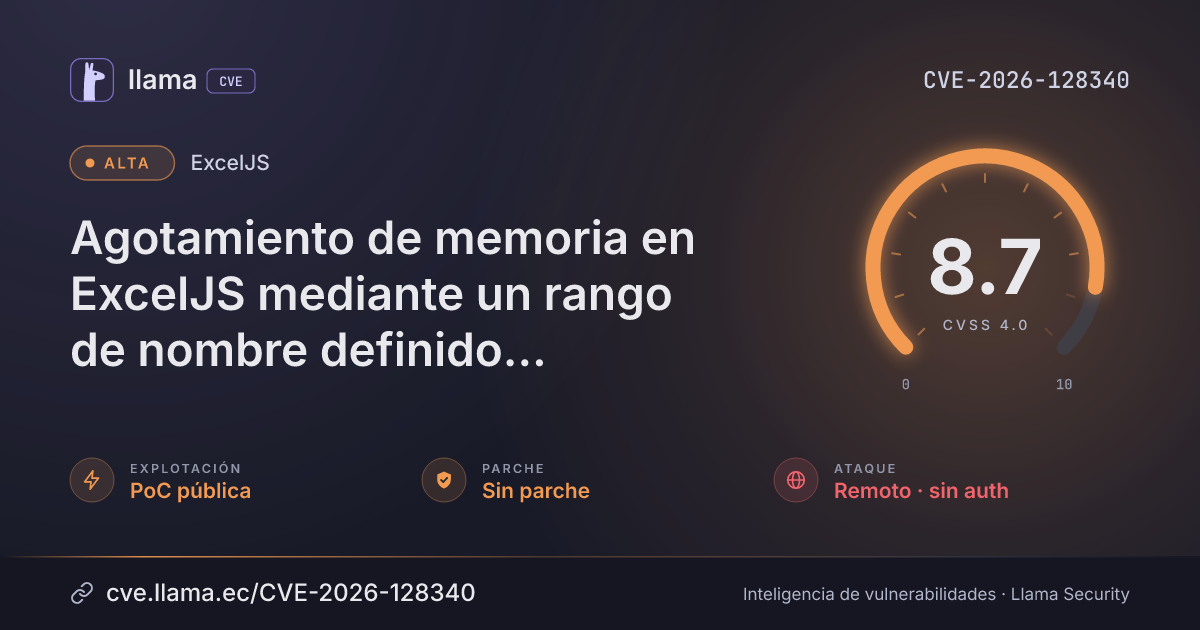
CVE-2026-128340

ExcelJS memory exhaustion via oversized defined name range

An attacker can crash an application that loads a crafted spreadsheet by making it run out of memory.

Afecta la configuración por defectoSin parche publicadodenial of service
Descargar PNG JSON
CVSS 4.0
8.7
Alta
CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:N/VI:N/VA:H/SC:N/SI:N/SA:N Fuente: CNA
ExplotaciónPoC públicaSSVC: PoC · no figura en CISA KEV
Exploits públicos0CISA-ADP reporta PoC; aún sin enlace público
ParcheSin parcheEl fabricante no ha publicado corrección
Exposición7 dDesde la divulgación, 13 nov 2026, 4:33 a. m.
Detección7 minDesde la divulgación hasta su ingreso al índice
Decisión SSVCSeguir de cerca
Monitorear y programar la remediación
Existe PoC pública, automatizable e impacto técnico parcial. No hay versión corregida: aplique mitigaciones.
Timeline

Ciclo de vida de la vulnerabilidad

Hoy
Divulgación
Publicada +2
Explotación
Remediación
Monitoreo
Detectada +2
Fuente: OSV
Verificada
13 nov 26
15 nov 26
16 nov 26
21 nov 26
13 nov 26
15 nov 26
17 nov 26
19 nov 26
21 nov 26
FechaFaseEventoDetalle
Divulgación Publicada CVE-2026-128340 divulgada · CVSS 8.7 (CNA)
Monitoreo Detectada Ingresó al índice
Monitoreo Fuente: NIST NVD Registro visto por primera vez en NIST NVD
Monitoreo Fuente: ENISA EUVD Registro visto por primera vez en ENISA EUVD
Divulgación Evaluación SSVC CISA-ADP · explotación PoC pública
Divulgación Modificada Última actualización del registro
Monitoreo Fuente: OSV Registro visto por primera vez en OSV
Monitoreo Verificada Última verificación contra las fuentes
Resumen

ExcelJS through 4.4.0 contains a memory exhaustion vulnerability that allows attackers to crash applications by supplying a workbook with an oversized defined-name range. DefinedNames.addEx expands ranges such as S!$A$1:$XFD$1048576 from xl/workbook.xml cell by cell, causing an uncatchable fatal heap out-of-memory error during xlsx.load().

Affects ExcelJS through 4.4.0 when loading a workbook with a defined name whose cell range covers a whole sheet. No fixed version is listed in the checked facts.

¿Qué significa?ExcelJS expands a defined name range such as S!$A$1:$XFD$1048576 from the workbook's xl/workbook.xml cell by cell, which can exhaust memory. Node.js then aborts with an out-of-memory error that cannot be caught, so the whole process goes down.
¿Quién está afectado?ExcelJS through 4.4.0 is affected. To check a project, look at the exceljs version in its installed dependencies, and check whether the workbooks it loads contain a defined name whose range covers a whole sheet.
¿Qué hacer?The checked facts name no fixed version and no patch identifier, so no upgrade target can be given. Check the ExcelJS project for a release newer than 4.4.0.
no-patchThe checked facts give no workaround. Until a fix is available, avoid loading workbooks from untrusted sources with ExcelJS.
Contexto

Condiciones y alcance

Condiciones necesarias para que el fallo sea explotable
01
ExcelJS through 4.4.0 is affected.“ExcelJS through 4.4.0 contains a memory exhaustion vulnerability”
02
The loaded workbook has a defined name whose cell range covers a whole sheet, such as S!$A$1:$XFD$1048576 in xl/workbook.xml.“DefinedNames.addEx expands ranges such as S!$A$1:$XFD$1048576 from xl/workbook.xml cell by cell”
¿Quién debe revisar?Teams running ExcelJS 4.4.0 or earlier that call xlsx.load() on untrusted .xlsx files, such as upload or import services.
Vector CVSS 4.0

Desglose de métricas

Opción resaltada = valor del vector · izquierda = peor caso · CNA
Vector de ataqueAV:N
RedAdyacenteLocalFísica
ComplejidadAC:L
BajaAlta
Requisitos de ataqueAT:N
NingunoPresentes
PrivilegiosPR:N
NingunoBajosAltos
InteracciónUI:N
NingunaPasivaActiva
Confid. (sistema)VC:N
AltoBajoNinguno
Integridad (sistema)VI:N
AltoBajoNinguno
Disponib. (sistema)VA:H
AltoBajoNinguno
Confid. (posterior)SC:N
AltoBajoNinguno
Integridad (posterior)SI:N
AltoBajoNinguno
Disponib. (posterior)SA:N
AltoBajoNinguno
Score de explotaciónQué tan fácil y probable es que la exploten
10.0/ 10Muy alto
Vector 10.0 (muy fácil) · sin evidencia de explotación.
Versiones

Rangos afectados

Afectada Corregida Última
exceljs≤ 4.4.0
4.4.0
Remediación

Estado del parche por paquete

Paquete / productoEstadoCorregida enDesde divulgaciónÚltima versión
npmexceljs
Sin parche — — 4.4.0 afectada
Explotación

Arsenal público

Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.

Referencias
Fabricantehttps://github.com/mateocallec/exceljs-hardened/security/advisories/GHSA-qvh4-wwpm-ggc8
Otrahttps://github.com/exceljs/exceljs
Otrahttps://github.com/exceljs/exceljs/blob/v4.4.0/lib/utils/cell-matrix.js#L28-L37
Otrahttps://github.com/exceljs/exceljs/blob/v4.4.0/lib/doc/defined-names.js#L182-L193
Otrahttps://www.vulncheck.com/advisories/exceljs-through-4.4.0-memory-exhaustion-via-oversized-defined-name-range

Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.