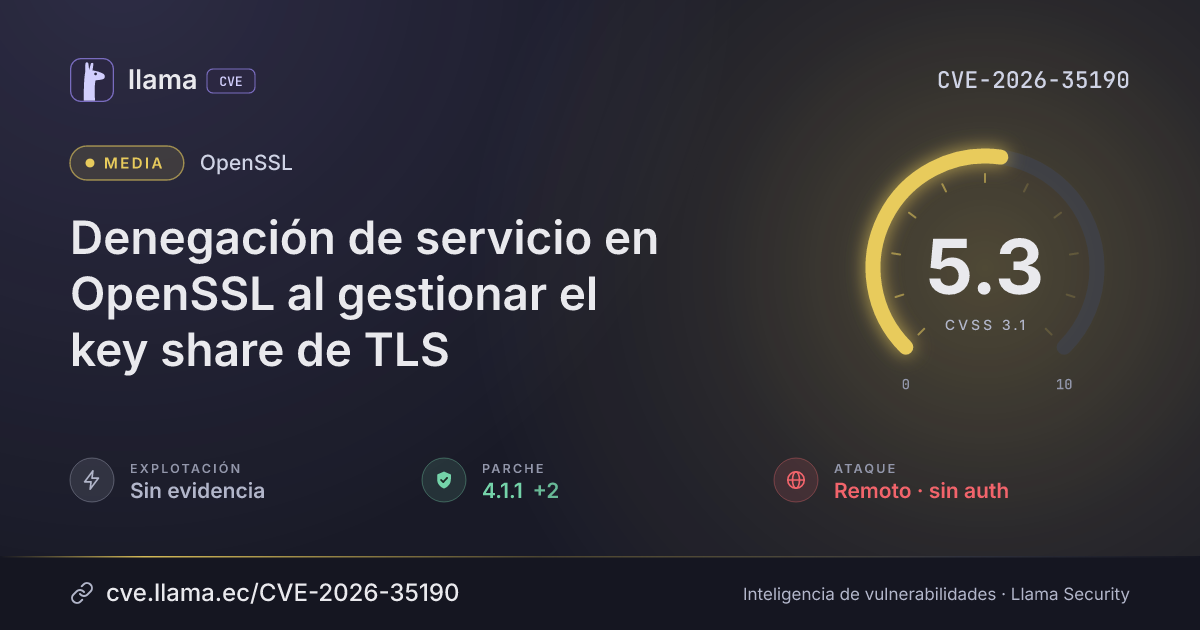
CVE-2026-35190
OpenSSL denial of service in TLS key-share handling
A remote attacker can crash a server with a crafted ClientHello, but only if the Suite B certificate flag is set.
CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:N/A:N
Fuente: CISA-ADP
Ciclo de vida de la vulnerabilidad
| Fecha | Fase | Evento | Detalle |
|---|---|---|---|
| Divulgación | Publicada | CVE-2026-35190 divulgada · CVSS 5.3 (CISA-ADP) | |
| Monitoreo | Detectada | Ingresó al índice | |
| Monitoreo | Fuente: NIST NVD | Registro visto por primera vez en NIST NVD | |
| Monitoreo | Fuente: ENISA EUVD | Registro visto por primera vez en ENISA EUVD | |
| Divulgación | Evaluación SSVC | CISA-ADP · explotación ninguna | |
| Divulgación | Modificada | Última actualización del registro | |
| Monitoreo | Verificada | Última verificación contra las fuentes |
A flaw in OpenSSL's TLS 1.3 key-share handling lets a remote client send a crafted ClientHello that makes the server read past the end of a static array, which can crash the process and cause a denial of service. It affects only servers that set the Suite B certificate flag with TLS 1.3 enabled, a non-default setup, and no memory contents are disclosed.
Descripción original del registro (openssl)
Issue summary: A server configured with the Suite B certificate flag through SSL_CTX_set_cert_flags() and with TLS 1.3 enabled may read past the end of a fixed group list when it processes a ClientHello whose supported_groups and key_share contain no Suite B group. Impact summary: A remote client can send a ClientHello that makes the server read past the end of a static array. The values read are never returned to the client, so no memory is disclosed; on builds with sanitizers or hardened allocators the read may crash the process, causing Denial of Service. CWE: CWE-125: Out-of-bounds Read Description: When the Suite B certificate flag is set, OpenSSL restricts the accepted groups to P-256 and P-384 by substituting a fixed two-element list for the configured group list. The tuple machinery used for key-share selection was not updated for this substitution: tls1_get_group_tuples() still returns the configured tuples, which by default describe eight groups. The server-side walk in tls_parse_ctos_key_share() then advances through the two-element list using those tuple counts without checking the cumulative offset against the number of groups present. Only applications that call SSL_CTX_set_cert_flags() with SSL_CERT_FLAG_SUITEB_128_LOS and leave TLS 1.3 enabled are affected. The openssl s_server -suiteB_128 option sets an X.509 verification parameter instead, so the stock command line server is not vulnerable. Default configurations do not reach this code. A client that offers only groups outside the Suite B set, such as X25519, forces every tuple to be walked and the read to run past the array. The bytes read are compared against client group IDs and never sent back, so no memory is disclosed. On builds with address sanitizers or hardened allocators the read can abort the process; in ordinary release builds it reads a few bytes of adjacent constant data. FIPS impact: no The affected code is outside the FIPS module boundary.
Desglose de métricas
Rangos afectados
Estado del parche por paquete
| Paquete / producto | Estado | Corregida en | Desde divulgación | Última versión |
|---|---|---|---|---|
OpenSSL |
Corregida | 3.5.10, 4.0.4, 4.1.1 | — | — |
3.5.104.0.44.1.1Arsenal público
Sin exploits, módulos ni PoC públicos conocidos a la fecha de verificación.
https://openssl-library.org/news/secadv/20261117.txthttps://github.com/openssl/openssl/commit/ade64619df04056b3e5fd1c1befe9425a7c80eb6https://github.com/openssl/openssl/commit/9a812981b927c5714b7c2e5d138618105cea2152https://github.com/openssl/openssl/commit/9491b0d9cc7950af1f3dc89499bd5433b9cd4f43Las referencias externas se muestran para copiar: cve.llama.ec no lo redirige a otros sitios.